For many government contractors, the words “CMMC audit” immediately trigger one concern: Will this disrupt our business? Between contract deadlines, system uptime requirements, and daily operational demands, compliance can feel like a threat to productivity. The reality, however, is that with the right structure and planning, preparing for a CMMC audit can be methodical, controlled, and far less disruptive than most teams fear.
Quick Answer
Most CMMC Level 2 failures are not technical failures. They are documentation failures: a control was operating, but no artifact proved it. Preparation breaks into four stages: a gap assessment against the 110 NIST 800-171 controls, remediation prioritized by assessment risk, documentation of the System Security Plan and Plan of Action and Milestones, and an internal readiness review before a C3PAO assessment. Most of the work runs against the existing Microsoft 365 and Azure configuration rather than against daily operations, so production keeps running while the evidence is assembled. The organizations that pass cleanly treat the assessment as a record-keeping problem with an engineering backbone: every control claim has an artifact behind it.
Before diving into preparation, it’s important to understand what a CMMC audit is truly designed to assess. Clarity reduces panic, and helps teams avoid unnecessary operational overhauls.
Under CMMC 2.0 compliance, the Department of Defense simplified the original framework into three levels aligned with existing federal standards. These levels range from basic safeguarding requirements to more advanced security maturity expectations.
For most defense contractors handling Controlled Unclassified Information (CUI), Level 2 is the focus. That means alignment with NIST SP 800-171 becomes central to preparation.
Level 2 requires contractors to implement and document 110 security controls outlined in NIST SP 800-171. These controls cover areas like access control, incident response, audit logging, configuration management, and encryption.
A CMMC audit at this level evaluates not just whether controls exist, but whether they are consistently implemented, documented, and functioning as intended.
Contrary to common belief, auditors are not looking to “trip up” organizations. During a CMMC audit, assessors evaluate:
They are assessing maturity and reliability, not perfection. Understanding this distinction helps organizations prepare strategically instead of reactively.
A CMMC audit becomes disruptive only when preparation lacks structure. Many operational slowdowns stem from poor planning rather than the compliance requirements themselves.
When companies delay preparation, they often rush to deploy tools, tighten permissions, or introduce new monitoring systems all at once. This reactive approach can interrupt workflows, lock users out of systems, or create confusion.
Security layered in thoughtfully is manageable. Security bolted on under pressure creates friction.
One of the biggest stressors before a CMMC audit is documentation. Without a gradual documentation process, teams end up scrambling to assemble policies, procedures, system diagrams, and evidence.
This documentation sprint often pulls IT teams away from production support and active contracts.
Compliance touches more than IT. Operations, HR, finance, and executive leadership all play a role in DOD cybersecurity compliance. When communication is siloed, security updates may surprise teams and cause workflow interruptions.
Compliance should align with business operations, not sit on top of them awkwardly. Organizations that treat CMMC 2.0 compliance as a separate side project often end up duplicating work and overcomplicating systems.
The key to a smooth CMMC audit is adopting a phased, structured plan that integrates into daily operations rather than overwhelming them.
Preparation begins quietly and strategically.
A formal gap assessment evaluates existing security controls against NIST SP 800-171 requirements. This phase identifies what already works and where improvements are needed.
Instead of immediately changing systems, teams document findings and create a prioritized roadmap. Planning first prevents unnecessary operational changes.
Not all gaps carry equal risk. A structured approach tackles high-impact items first.
Risk-based remediation focuses on:
By sequencing remediation efforts logically, organizations avoid overwhelming internal teams and maintain operational continuity during the CMMC audit preparation process.
Tools don't transform organizations. Governed execution models do. i3solutions delivers enterprise digital transformation services that start with the operating model, governance structure, and delivery accountability required to produce outcomes the executive team can measure and defend.
Assess i3solutions Digital Transformation ServicesDocumentation should never be a last-minute effort. Instead of waiting until right before a CMMC audit, organizations should gradually develop:
Building these artifacts over time eliminates panic and prevents disruption.
Before undergoing a formal CMMC audit, internal mock assessments provide invaluable insight. These dry runs:
An internal readiness review helps reduce uncertainty and ensures teams are prepared without scrambling.
Compliance preparation does not need to derail productivity. With a few operational guardrails, disruption can be minimized.
Security updates, MFA rollouts, or system changes should occur during planned maintenance windows. Aligning improvements with business cycles reduces friction.
Transparency reduces resistance. If teams understand why changes are happening, and how they protect contracts, they are far more likely to support CMMC 2.0 compliance initiatives.
Every control should have a defined owner. Ambiguity causes delays and duplicated effort. Clear ownership ensures smoother preparation for a CMMC audit.
One common mistake is implementing overly complex solutions. The goal of a CMMC audit is reasonable assurance, not unnecessary technological complexity.
Simple, well-documented solutions often outperform intricate systems that confuse users.
Certain missteps almost guarantee operational strain during CMMC audit preparation.
Procrastination forces reactive decision-making. Beginning early allows incremental improvements instead of emergency overhauls.
DOD cybersecurity compliance affects the entire organization. Without executive and operational alignment, IT teams carry the burden alone, leading to burnout and mistakes.
Documentation is not an afterthought. A delayed documentation strategy leads to frantic evidence collection just before a CMMC audit.
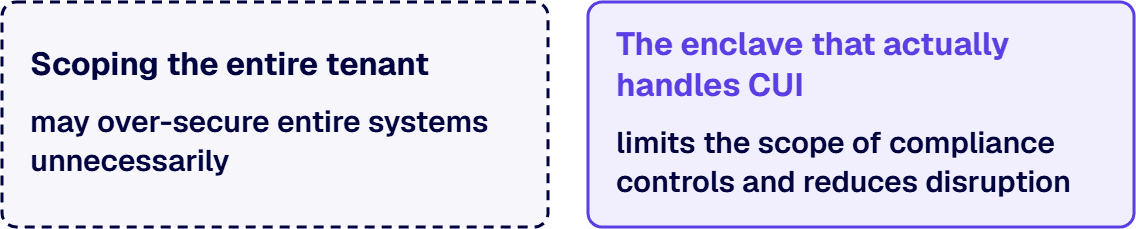
If CUI environments are poorly scoped, organizations may over-secure entire systems unnecessarily. Proper boundary definition limits the scope of compliance controls and reduces disruption.
Security controls are only effective if employees understand them. User adoption training reduces confusion, minimizes helpdesk spikes, and supports operational stability.
There is a point where internal teams may need additional guidance, not because they lack capability, but because the complexity of a CMMC audit demands structure.
Signs your internal teams are overwhelmed include:
These are signals that structured support may be necessary.
External experts can provide phased remediation plans aligned with operational schedules. Instead of guessing at sequencing, organizations receive a prioritized roadmap tailored to their environment.
An experienced compliance partner helps:
A CMMC audit does not have to derail your operations. When preparation is phased, strategic, and aligned with business processes, compliance becomes manageable rather than disruptive.
By understanding what assessors evaluate, addressing risks incrementally, documenting gradually, and aligning stakeholders early, government contractors can meet CMMC 2.0 compliance requirements without compromising uptime or productivity.
i3solutions serves as a calm, experienced partner for organizations navigating DOD cybersecurity compliance. With structured assessments, practical remediation planning, and operationally sensitive guidance, i3solutions helps contractors prepare for a CMMC audit with clarity, confidence, and continuity, ensuring security strengthens your business instead of slowing it down.
Justin has spent more than 15 years at i3solutions and more than 25 years leading project, program, and product delivery across complex technology environments. His work centers on turning strategy into governed execution, aligning technical teams and stakeholders, managing delivery risk, and guiding Microsoft 365, SharePoint, Power Platform, cloud, data, automation, and custom application programs through measurable production outcomes.
View LinkedIn ProfileFour stages: a gap assessment mapping the environment against the 110 NIST 800-171 controls, remediation prioritized by assessment risk, documentation of the System Security Plan (SSP) and Plan of Action and Milestones (POA&M), and an internal readiness review before a C3PAO assessment. The bulk of the effort is evidence and configuration, not new tooling.
In most cases, yes. Preparation works against the configuration and documentation layer of the existing Microsoft 365 and Azure environment, so production keeps running. Disruption tends to arrive when a gap assessment reveals that controlled unclassified information is being handled in an environment that was never scoped for it. Finding that late forces an emergency change. Finding it in the gap assessment does not.
The timeline is determined by two variables: how far the current Microsoft 365 and Azure configuration sits from the 110 controls, and how complete the existing documentation already is. An environment with governance in place, including configured audit logging, enforced access control, and defined data boundaries, can move through preparation in roughly three to six months. An environment where those controls have to be retrofitted from scratch typically runs six to twelve months or more. The gap assessment converts that range into a defensible project schedule with named milestones.
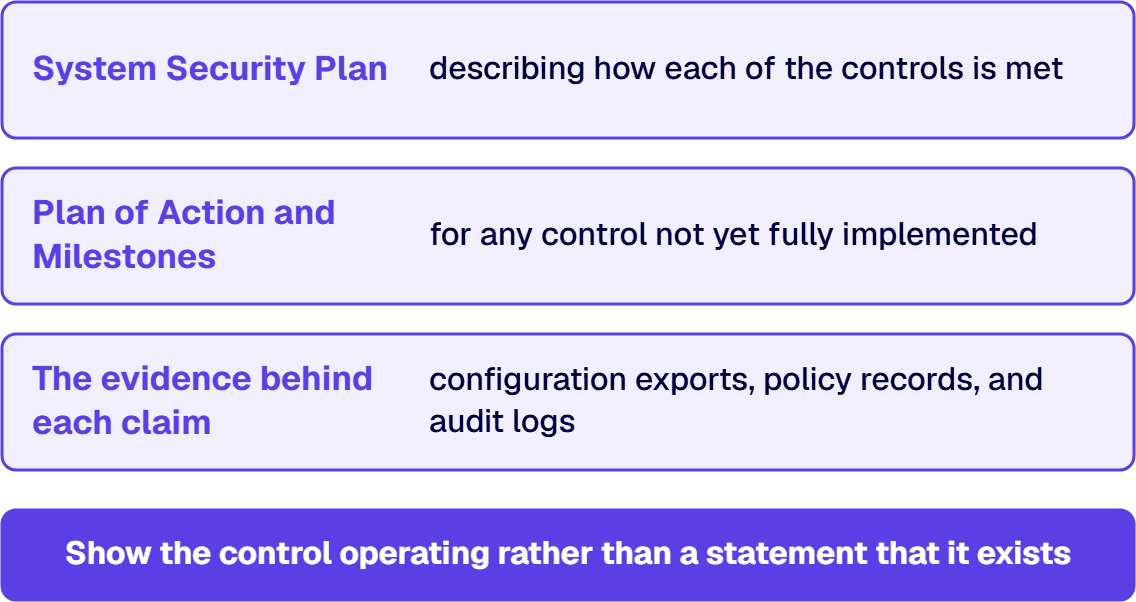
A System Security Plan describing how each of the 110 controls is met, a Plan of Action and Milestones for any control not yet fully implemented, and the evidence behind each claim: configuration exports, policy records, and audit logs that show the control operating rather than a statement that it exists.
Before the C3PAO, not during. i3solutions’ US-based senior architects, with no offshore or nearshore handoff, verify the Microsoft 365, Azure, and Power Platform configuration against the control requirements and confirm the evidence reads the way an assessor will read it. That verification produces a defensible evidence package before the assessment begins, so control gaps are found and closed on your schedule rather than surfaced in the assessment room. It is also the due-diligence trail a board or audit committee expects to see, regardless of the assessment outcome.
Three patterns surface consistently. First, treating CMMC as a tooling purchase rather than a governance and documentation exercise. Second, scoping the entire tenant instead of the enclave that actually handles CUI. Third, leaving audit log retention and access control until last, when they are the hardest controls to produce evidence for after the fact.


Most enterprise digital transformation initiatives stall not because the technology is wrong, but because there's no governing framework connecting the investment to measurable outcomes. i3solutions' senior digital transformation advisors work with IT leaders who've recognized that the initiative needs structural intervention, not another planning cycle.
Talk to a Digital Transformation Advisor
US-Based Microsoft System Integrator | Est. 1997
© i3solutions. All rights reserved.
US-Based Microsoft System Integrator | Est. 1997
© i3solutions. All rights reserved.


