Okta vs Entra ID: What’s the Difference for Enterprise IT?

Okta vs Entra ID: what’s the difference comes down to where your identity already lives, not to a feature checklist. Entra ID is the lower-integration-risk default for Microsoft-centric estates because Microsoft 365, Azure, and Intune already trust it as their identity plane, so you govern one model instead of brokering two. Okta earns its place when you run a large non-Microsoft SaaS portfolio or an Okta investment that already works. The expensive mistake is running both without deciding which is authoritative, which leaves access ungoverned across the seam, and that is the question this guide settles for your estate.
Microsoft’s Entra ID emerges as a critical player in navigating the intricacies of digital identity verification. Its seamless integration within the extensive Microsoft ecosystem, robust analytics leveraging AI and machine learning, and steadfast commitment to the latest cybersecurity standards position it as a front-runner in the IAM space. Okta, on the other hand, is platform-agnostic, offering extensive integrations with a wide range of third-party applications and services, making it a versatile choice for diverse IT environments. These differences make Okta suitable for varied IT landscapes, while Entra ID is ideal for businesses deeply invested in Microsoft technologies.
Key Takeaways
- For enterprises already invested in Microsoft 365, Azure, Power Platform, or Dynamics 365, Microsoft Entra ID is typically the stronger choice: it is already included in M365 licensing, integrates natively with Conditional Access and Intune, and supports CMMC, FedRAMP, and HIPAA compliance frameworks.
- Okta remains the better fit for multi-vendor environments with large non-Microsoft SaaS portfolios, with 7,000+ pre-built integrations in the Okta Integration Network that provide clear operational advantage for complex non-Microsoft app estates.
- Many regulated enterprises run both platforms simultaneously: Entra ID governing the Microsoft stack internally, Okta managing external identities and non-Microsoft SaaS federation. This coexistence model often represents the optimal architecture.
- For U.S. defense and aerospace contractors under CMMC, ITAR, or FedRAMP High requirements, Entra ID in a GCC High environment is structurally required: Okta states that it holds “FedRAMP High and Moderate authorizations” and that Okta for US Military “has earned its U.S. Department of Defense Impact Level 5 (IL5) Provisional Authorization to Operate”.
- For Microsoft 365 customers, Entra ID is already included in their subscription at zero additional per-user cost: consolidating identity from Okta to Entra ID eliminates $70,000+ in annual Okta licensing spend for a 1,000-user organization, offset by the cost of whichever Entra ID tier you license.
- Entra ID is the native identity provider for Power Platform, Dynamics 365, and Microsoft Copilot Studio: organizations running Okta as their primary identity provider in a Power Platform environment typically need Entra ID in parallel regardless.
Quick Answer
Okta vs Microsoft Entra ID: For enterprises already invested in Microsoft 365, Azure, Power Platform, or Dynamics 365, Microsoft Entra ID is typically the stronger choice: it is already included in M365 licensing, integrates natively with Conditional Access and Intune, and supports CMMC, FedRAMP, and HIPAA compliance frameworks. Okta remains the better fit for multi-vendor environments with large non-Microsoft SaaS portfolios. Many regulated enterprises run both: Entra ID governing the Microsoft stack, Okta managing external identities.
Enhance security and streamline access management with i3solutions’ expert Okta consulting services, offering tailored solutions for seamless integration and robust protection.
When it comes to protecting your enterprise, selecting the right identity and access management solution is a critical decision. The choice between Okta vs Entra ID depends on factors including company size (the scale of your workforce dictates the level of service complexity and performance you require) and integration needs, specifically the range of third-party services your enterprise uses and the ease with which the IAM solution can be integrated.
Microsoft Entra ID is the product Microsoft formerly named Azure Active Directory (Azure AD). Microsoft’s own rename page states that “Microsoft renamed Azure Active Directory (Azure AD) to Microsoft Entra ID”, and its table of service plan names maps Azure Active Directory Premium P1 to Microsoft Entra ID P1 and Azure Active Directory Premium P2 to Microsoft Entra ID P2, noting that “Service plan display names changed on October 1, 2023.” Readers comparing Azure AD or Azure AD Premium with Okta are comparing the same product this page covers. (Source: Microsoft Learn, “New name for Azure Active Directory”, learn.microsoft.com/en-us/entra/fundamentals/new-name, read date 2026-09-22.)
Okta vs Microsoft Entra ID: Feature-by-Feature Comparison
Both platforms deliver enterprise-grade identity and access management, but their architectures reflect fundamentally different design philosophies. Okta is built as a vendor-neutral identity and authentication hub. Microsoft Entra ID is built as the identity layer for the Microsoft cloud. The right choice depends on which stack your organization is already running.
Okta: ~$6/user/month base; $15+/user for advanced features
Entra ID: Included in M365 E3/E5; P1 in Business Premium
Entra ID: significant cost advantage for existing M365 customers
Okta: 7,000+ pre-built integrations (Okta Integration Network)
Entra ID: Deep Microsoft integration; broad SAML/OIDC support
Okta for large non-Microsoft SaaS estates
Okta: Per-app policies with granular rules; strong multi-vendor control
Entra ID: Tenant-wide unified policy engine; integrates with Intune for device compliance
Entra ID for Microsoft-managed device fleets
Okta: Requires additional federation configuration
Entra ID: Native. No additional configuration required
Entra ID: clear advantage for Power Platform environments
Okta: Requires on-premises agents; synchronization complexity
Entra ID: Native Cloud Sync and Connect Sync; minimal on-premises dependency
Entra ID for organizations with existing AD infrastructure
Okta: Universal Directory handles external orgs cleanly
Entra ID: Entra External ID (formerly B2B/B2C); improving but more complex
Okta for complex multi-org external identity federation
Okta: SOC 2, ISO 27001, HIPAA, FedRAMP Moderate (Okta’s commercial cloud); Okta for Government High holds FedRAMP High and Okta for US Military holds a DoD IL5 provisional authorization
Entra ID: SOC 2, ISO 27001, HIPAA, FedRAMP High, CMMC, DoD IL2 to IL4 through GCC High (IL5 through the separate DoD environment, which Microsoft states is “certified as DoD SRG L5”)
Entra ID: stronger for U.S. federal and defense requirements
Okta: Requires additional integration work
Entra ID: Native. Entra ID is required for Copilot licensing and governance
Entra ID: no alternative for Copilot deployments
Okta vs Microsoft Entra ID on Enterprise Security and Identity Management Scope
Your enterprise security posture should sit on the platform whose policy surface already governs sign-in, device state and session risk for the systems you most need to protect, not on the one with the longer feature list. Okta enforces policy per application across a multi-vendor estate, so it governs sign-in strength and session behavior consistently wherever the application lives. Entra ID enforces policy through one tenant-wide engine, so it governs sign-in alongside the device compliance state and risk signals already collected in that tenant. Both enforce strong authentication, which is why a feature comparison rarely settles this. The question that settles it for a VP of IT is narrower: which platform already holds the signals your security team acts on during an investigation, and which one would have to be fed them by something else.
Identity management compares only one layer at a time, because the phrase covers four separate jobs: the authoritative directory that holds the account of record, the joiner-mover-leaver lifecycle that creates, changes and removes access, the application catalogue and single sign-on estate, and privileged access to the systems an attacker would want most. On the directory layer, the natural owner is whichever platform your accounts are already mastered in. On lifecycle, it is whichever platform your HR system and your joiner-mover-leaver process already write into. On the application catalogue, Okta is the natural owner of a broad non-Microsoft software estate and Entra ID is the natural owner of the Microsoft estate. On privileged access, it is whichever platform issues the standing administrative roles for the systems that matter most. So the deciding question is not which product manages identity better: it is where your authoritative directory already sits, and what governs joiner-mover-leaver today. Where those two answers point at different platforms, settle the directory layer first, because the other three inherit from it.
When to Choose Entra ID vs Okta: A Decision Framework for Enterprise IT
The decision between Okta and Microsoft Entra ID is rarely about which platform is technically superior. It is about which platform reduces operational risk and governance complexity in your specific environment.
- Already using Microsoft 365, Azure, or Power Platform: Entra ID is already in your M365 subscription. Deploying Okta on top creates redundant licensing and integration overhead.
- Running Power Platform, Dynamics 365, or Copilot: Native integration with the Power Platform security model and Dataverse row-level security. Okta requires additional federation work.
- Subject to CMMC, ITAR, FedRAMP, or GCC High requirements: CMMC certification requires GCC High, which is purpose-built for U.S. federal and defense compliance. Okta states that “Okta’s DoW IL5 authorized Identity platform supports Controlled Unclassified Information and National Security Systems (NSS).”
- Managing a large Windows device fleet with Intune: Entra ID + Intune device compliance is a native, tightly governed pairing. Okta device trust requires additional configuration and certificates.
- Running a diverse SaaS portfolio (Salesforce, Workday, Zoom, ServiceNow): Okta Integration Network provides 7,000+ pre-built connectors. Entra ID SAML/OIDC support is broad but less mature for non-Microsoft SaaS.
- Managing multi-tenant or external partner federation at scale: Okta Universal Directory handles complex multi-org federation more cleanly than Entra External ID.
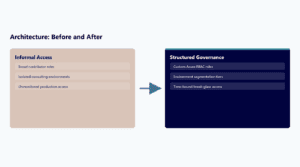
Your organization has a Microsoft-heavy internal stack but also manages complex external identity needs or a broad non-Microsoft SaaS portfolio. The common pattern: Entra ID governs the Microsoft stack internally; Okta manages external identities and non-Microsoft SaaS federation. The key is defining clear boundaries upfront: which directory owns which identity type, how provisioning flows are sequenced, and how Conditional Access policies interact across both platforms.
The practitioner community captures this well: the right answer always comes down to whether the platform’s gaps are your gaps. For enterprises deeply invested in the Microsoft stack, Entra ID’s gaps rarely align with their actual operational priorities. The cost savings alone from eliminating redundant Okta licensing typically justify a consolidation strategy.
Entra ID vs Okta for Regulated Industries: CMMC, FedRAMP, ITAR, and HIPAA
For enterprises operating in regulated environments, the IAM platform decision carries compliance implications that extend well beyond feature comparison. This is the dimension most general comparisons overlook, and where Microsoft Entra ID holds a structural advantage for U.S. defense, aerospace, financial services, and healthcare organizations.
✅ Entra ID: GCC High; Microsoft 365 GCC High environment, purpose-built for defense contractors
⚠️ Okta: Supports MFA and access control but lacks native GCC High environment
Defense contractors pursuing CMMC certification should be on GCC High, which requires Entra ID
✅ Entra ID: GCC High provides FedRAMP High + ITAR-boundary controls
⚠️ Okta: FedRAMP Moderate (Okta’s commercial cloud) does not satisfy ITAR data residency requirements; Okta’s separate government offerings, Okta for Government High and Okta for US Military, hold FedRAMP High and a DoD IL5 provisional authorization.
Aerospace and defense manufacturers handling CUI/ITAR data must restrict identity data to U.S. citizens on U.S. soil
✅ Entra ID: Native. Entra ID GCC High is FedRAMP High authorized
⚠️ Okta: FedRAMP High and Moderate authorized, per Okta
Federal agencies and contractors requiring FedRAMP High can use Entra ID in GCC High or Okta for Government High
✅ Entra ID: Microsoft signs BAA; Conditional Access + PIM for audit trails
✅ Okta: Signs BAA; supports HIPAA-aligned access policies
Both platforms support HIPAA; Entra ID preferred in M365-based healthcare environments
✅ Entra ID: PIM, access reviews, Separation of Duties built-in
✅ Okta: Access certifications, governance workflows available
Both viable; Entra ID PIM preferred for Microsoft-based financial workflows (Dynamics 365, Power Platform)
If your organization handles Controlled Unclassified Information (CUI), is pursuing CMMC certification, or operates under ITAR export control requirements, Microsoft Entra ID within a GCC High environment is not simply a preference. It is an architectural requirement. Okta’s public sector page states: “Okta’s FedRAMP High authorized Identity platform supports high impact systems and data.” Okta’s 21 July 2026 release states that Okta for US Military “has earned its U.S. Department of Defense Impact Level 5 (IL5) Provisional Authorization to Operate” and describes “standardizing IL4 and IL5 workloads within a single cloud environment”.
i3solutions has deep experience implementing identity governance for enterprises in aerospace and defense manufacturing, financial services, and healthcare, including environments with CMMC and ITAR obligations. Our team designs IAM architectures that satisfy security requirements and hold up under audit, without creating operational friction for end users.
Okta vs Entra ID Cost Comparison: Licensing, Migration, and Real TCO
Licensing cost is often the first number IT leaders examine when comparing these platforms, but the true cost comparison includes migration effort, operational overhead, and the value of consolidating tools you already own.
- Base License: ~$6/user/month (Workforce Identity Cloud)
- Advanced Governance: $15+/user/month with lifecycle management add-ons
- M365 Incremental Cost: Full per-user cost on top of existing M365 spend
- Integration Effort: Lower for large non-Microsoft SaaS (pre-built connectors)
- Operational Overhead: Separate admin console; additional identity platform to maintain
- Base License: Included in M365 Business Premium, E3, and E5
- Advanced Governance: Entra ID P2 included in M365 E5; ~$9/user add-on to E3
- M365 Incremental Cost: Zero (already paying for it)
- Integration Effort: Near-zero for Microsoft stack; moderate for non-Microsoft apps
- Operational Overhead: Unified with Azure Portal and Microsoft 365 Admin Center
For most Microsoft-centric enterprises, the total cost of running Okta on top of an existing M365 subscription represents significant redundant spend. Recent Okta price increases on the Customer Identity Cloud product have accelerated the migration conversation for many IT directors. The cost savings from eliminating Okta licensing, combined with reduced operational overhead from a single identity platform, typically deliver a compelling ROI for consolidated Entra ID strategies.
Can Okta and Microsoft Entra ID Work Together?
Yes, and in complex enterprises, running both platforms simultaneously is not a compromise; it is often the optimal architecture. The most common enterprise IAM pattern we see in Microsoft-heavy environments with broad SaaS portfolios combines the strengths of both platforms.
- Microsoft Entra ID governs internal workforce identity: Microsoft 365, Azure, Power Platform, Dynamics 365, SharePoint, Teams, and all managed Windows devices via Intune Conditional Access.
- Okta manages external identities, customer-facing CIAM scenarios, and non-Microsoft SaaS federation where the Okta Integration Network provides clear operational advantage.
This architecture avoids forcing a single platform to cover every identity use case, and it preserves investment in either platform without creating governance gaps. The key is defining clear boundaries upfront: which directory owns which identity type, how provisioning flows are sequenced, and how Conditional Access policies interact across both platforms. Sequencing those provisioning and directory flows cleanly often calls for broader system integration and data management solutions alongside the identity platforms themselves.
i3solutions designs and implements IAM architectures for enterprises navigating exactly this decision, including environments where Okta is already deployed and needs to coexist cleanly with a growing Entra ID footprint as Microsoft stack adoption expands.
What Breaks When Okta and Entra ID Are Both in Play
Short answer: when Microsoft Entra ID and Okta run side by side, the failures are not caused by having two identity platforms. They occur where both planes hold authority over the same object and no owner has been declared. Eight conditions are worth naming: two writers on one attribute, an access decision enforced by the plane that does not hold the data, two front doors for external identity, a leaver process that stops at the first directory, strong authentication registered twice and recovered once, entitlement groups authored in one plane and consumed in the other, audit evidence split across two logs with no shared identifier, and a federation trust with an expiry date and no rehearsal. Each one is a configuration decision with a defined answer rather than a platform defect.
- Two writers on one attribute. The condition is that both directories are permitted to write the same field, such as the user principal name, a group membership or a licence assignment. What breaks is that the last write wins, the two records drift apart, and no support ticket can be answered cleanly because neither record is authoritative. Close it by naming one system of record per attribute, setting the other platform to read only for that attribute, and reconciling on a fixed schedule instead of on complaint.
- The access decision is enforced by the plane that does not hold the data. The condition is an application that trusts one platform as its token issuer while the data it reaches sits in the estate governed by the other. What breaks is that the signals the data-holding plane relies on, device compliance state being the common example, are absent from the token the application accepted, so a session one policy engine would have refused is admitted by the other. Close it by inventorying every application against two facts, which platform issues its token and where its data lives, and making the plane that holds the data the plane that enforces the decision.
- External identity has two front doors. The condition is that both platforms can accept an external collaborator and neither has been declared the single entry point. What breaks is that the same partner exists as two identities with two lifecycles, or exists in one plane and not the other, so an access review run in one plane reports a clean sheet while the access is still live in the other. Close it by running every external invitation through one plane and federating from there, so external access carries one record and one expiry date.
- Deprovisioning stops at the first directory. The condition is a joiner, mover and leaver process that terminates an account in one directory with nothing fanning the change out to the other. What breaks is that the account reads as disabled in one plane while sessions, refresh tokens and application assignments stay live in the other. Close it by making termination fan out to both planes in a single step, and by testing it against the time to token invalidation on a real account rather than against the account status flag.
- Strong authentication is registered twice and recovered once. The condition is that each platform holds its own authenticator registration and its own self-service reset path. What breaks is that a help desk reset performed in one plane leaves the factors in the other untouched, so account recovery is only as strong as the weaker of the two flows. Close it by choosing one plane to own registration and recovery for strong authentication, routing the help desk procedure to that plane, and removing the second self-service reset path.
- Entitlement groups are authored in one plane and consumed in the other. The condition is that groups are synchronised between the platforms rather than owned by one of them. What breaks is that a rename, a nested group change or a membership rule edit made in the authoring plane silently changes who holds access in the consuming plane, with no approval step between the edit and the effect. Close it by naming the owning plane for each group, blocking edits to those groups in the other platform, and alerting on membership deltas rather than reviewing them on a quarterly cycle.
- Audit evidence is split across two logs with no shared identifier. The condition is that each platform writes its own sign-in and administrative records, under its own user identifiers and its own retention period. What breaks is that the question an auditor actually asks, who held access to what and when, requires joining two logs whose user records share no key, and that join gets attempted for the first time under audit pressure. Close it by fixing one immutable identifier that both planes carry on every record, exporting both logs into a single retained store, and rehearsing the join before the audit window opens.
- The trust between the two planes has an expiry date and no rehearsal. The condition is a federation trust carried by a signing certificate that expires, with no non-production tenant pair on which to rehearse the rotation. What breaks is that authentication for every application behind that trust stops at the moment of expiry, and the first rehearsal happens in production during the outage. Close it by holding an inventory of every federation trust with its certificate expiry date and a named owner, alerting well ahead of expiry rather than at it, and rehearsing rotation in a non-production pair.
The common thread across all eight is authority rather than technology. Each one is a question about which plane owns a decision, and each is closed the same way: decide once, write the decision down, and enforce it in configuration rather than in convention. The practical starting point is an inventory that lists every application with its token issuer, every synchronised attribute with its writer, every entitlement group with its author, and every federation trust with its expiry date and owner. Where that inventory is current and enforced, running both platforms is a deliberate architecture. Where it is not, the second platform is an undeclared dependency that nobody is watching.
Is Microsoft Entra ID the Right Alternative to Okta?
For an enterprise already standardized on Microsoft 365 and Azure, the usual alternative to Okta is Microsoft Entra ID, because the identity layer is largely already licensed and in place. For an estate whose applications are mostly outside Microsoft, it may not be, and a standalone identity provider built for heterogeneous estates can remain the better fit.
To decide which case describes your estate, apply the tests in the section above titled “When to Choose Entra ID vs Okta: A Decision Framework for Enterprise IT”, then weigh the licensing picture in the cost comparison section and the boundary questions in the sections on running both platforms together.
i3solutions regularly delivers Okta to Microsoft Entra ID migrations for enterprises. Where the tests point to consolidation, the next section sets out what the move involves.
Migrating from Okta to Microsoft Entra ID: What Enterprise IT Leaders Should Expect
Okta-to-Entra migrations have accelerated across regulated industries as enterprises consolidate their Microsoft investments and respond to Okta pricing changes. The migration is achievable but requires careful sequencing to avoid identity disruptions in production environments. i3Solutions provides dedicated Okta to Entra ID migration services that plan and sequence this transition without disrupting production access.
- Discovery and inventory: Document all applications federated through Okta, including authentication protocols (SAML, OIDC, LDAP), provisioning configurations, and Conditional Access policy equivalents.
- Entra ID environment design: Define tenant structure, directory sync strategy (Cloud Sync vs. Connect Sync), Conditional Access policy architecture, and device management integration with Intune.
- Application migration by risk tier: Migrate low-risk internal apps first, validate, then progress to business-critical applications. Maintain Okta as fallback during parallel operation windows.
- User migration and MFA re-enrollment: Migrate authentication methods with minimal disruption; communicate changes early to avoid service desk overload.
- Governance alignment: Map Okta access certifications and lifecycle management policies to Entra ID Privileged Identity Management, access reviews, and entitlement management.
The most common failure mode in Okta-to-Entra migrations is underestimating policy complexity. Organizations that have built granular per-application authentication policies in Okta over many years often discover that mapping these to Entra Conditional Access requires deliberate architectural decisions, not mechanical translation. Engaging an Okta implementation partner with direct Entra ID governance experience significantly reduces migration risk and timeline.
Frequently Asked Questions: Okta vs Microsoft Entra ID
What is the main difference between Okta and Microsoft Entra ID?
Okta is a vendor-neutral identity platform designed to manage access across any technology stack, with 7,000+ pre-built SaaS integrations. Microsoft Entra ID is Microsoft’s cloud identity platform, natively integrated with Azure, Microsoft 365, Power Platform, and Dynamics 365. For organizations already running the Microsoft stack, Entra ID is typically the more cost-effective and operationally simpler choice. For organizations with large non-Microsoft SaaS portfolios, Okta often provides better integration coverage.
Is Microsoft Entra ID free with Microsoft 365?
Yes, Microsoft Entra ID is included in Microsoft 365 Business Premium, E3, and E5 subscriptions. The P1 tier, which includes Conditional Access and self-service password reset, is included with Business Premium. The P2 tier, which adds Privileged Identity Management and access reviews, is included with M365 E5 or available as an add-on. For organizations already paying for M365, Entra ID represents zero additional licensing cost for core identity functions.
Can Okta be used with Microsoft 365 and Azure?
Yes, Okta integrates with Microsoft 365 and Azure through SAML and OIDC federation. However, some Microsoft features (including Conditional Access device compliance through Intune, Microsoft Copilot governance, and Power Platform row-level security) work natively only with Entra ID. Organizations using Okta as their primary identity provider alongside M365 typically run a hybrid architecture where Entra ID handles Microsoft-specific access controls while Okta manages the broader application portfolio.
Which IAM platform is better for regulated industries like defense, healthcare, or financial services?
For U.S. defense and aerospace contractors operating under CMMC, ITAR, or FedRAMP requirements, Microsoft Entra ID within a GCC High environment is structurally required: Okta states that it holds “FedRAMP High and Moderate authorizations” and that Okta for US Military “has earned its U.S. Department of Defense Impact Level 5 (IL5) Provisional Authorization to Operate”. For HIPAA-covered healthcare organizations already on Microsoft 365, Entra ID is preferred due to native integration with the M365 compliance stack. Both platforms support SOX and GDPR controls; the choice depends on whether the primary compliance workloads run on Microsoft infrastructure.
What is the cost difference between Okta and Microsoft Entra ID?
For Microsoft 365 customers, Entra ID is already included in their subscription at no additional per-user cost. Okta Workforce Identity starts at approximately $6 per user per month for the base tier, with lifecycle management and advanced governance features pushing costs to $15 or more per user per month. For a 1,000-user organization running M365 E3, consolidating identity to Entra ID from Okta eliminates $70,000+ in annual Okta licensing spend. Net savings are that figure less the cost of whichever Entra ID tier you license, and before accounting for reduced operational overhead from managing a single platform.
How difficult is it to migrate from Okta to Microsoft Entra ID?
Migration complexity depends on the breadth of the Okta deployment, specifically the number of federated applications, the sophistication of existing authentication policies, and the extent of lifecycle management automation. A straightforward migration for a Microsoft-centric organization with 20 to 30 federated applications can be completed in 60 to 90 days with proper planning. Complex environments with hundreds of app federations, custom Okta workflows, or external identity federation requirements may require 6 to 12 months and phased coexistence architecture.
Does Entra ID work with Power Platform and Dynamics 365?
Yes, and this is one of Entra ID’s strongest differentiators. Microsoft Entra ID is the native identity provider for Power Platform, Dynamics 365, and Microsoft Copilot Studio. Entra ID governs user access, row-level security in Dataverse, service principal authentication for Power Automate flows, and licensing assignment for Power Apps. Organizations running Okta as their primary identity provider in a Power Platform environment typically need to maintain Entra ID in parallel, making full Okta consolidation impractical in most Power Platform deployments.
Should we use Okta or Entra ID if we already have both?
The most effective architecture for Microsoft-heavy enterprises keeps Entra ID as the authoritative identity source for all Microsoft services: Microsoft 365, Azure, Power Platform, Dynamics 365, SharePoint, Teams, and managed devices via Intune. Okta remains in place for external identity federation, customer identity scenarios, and non-Microsoft SaaS applications where the Okta Integration Network provides clear operational advantages.
What is Microsoft Entra ID GCC High?
Microsoft Entra ID GCC High is a sovereign cloud deployment of Entra ID designed for U.S. federal agencies, defense contractors, and organizations handling Controlled Unclassified Information under ITAR or FedRAMP High requirements. It operates on physically separated infrastructure staffed by screened U.S. personnel, meeting the data residency and access control requirements for CMMC Level 2/3, FedRAMP High, and ITAR boundary compliance. Organizations pursuing CMMC certification or operating in the Defense Industrial Base should evaluate GCC High as a requirement, not an option.
If the Okta-versus-Entra decision is live in your organization, an identity and access management consultation maps both platforms against your licensing, your compliance load, and what you already own.