Microsoft 365 GCC High Migration Checklist: Best Practices for Defense Contractors

A GCC High migration checklist covers tenant eligibility validation, data and identity migration planning, compliance mapping to CMMC 2.0 and NIST SP 800-171, and post-migration governance, because GCC High is a full tenant rebuild in an isolated government cloud rather than an upgrade from commercial Microsoft 365. Defense contractors handling Controlled Unclassified Information should sequence the work in phases: confirm eligibility and licensing, inventory CUI and Active Directory dependencies, plan mailbox and SharePoint data migration, validate compliance controls, and stand up ongoing governance before cutover. i3Solutions plans and runs these migrations for regulated defense organizations, structuring each phase around the compliance evidence assessors expect.
Key Takeaways
- Complete tenant rebuild required: GCC High migration is not an upgrade path from commercial Microsoft 365. It requires rebuilding your entire tenant infrastructure in the isolated government cloud environment.
- 12-18 month implementation timeline: Organizations with complex Active Directory environments should plan for extended GCC High migration timelines that include assessment, eligibility validation, data migration, and post-migration governance phases.
- Licensing premium over Commercial: GCC High costs more than the equivalent Commercial Microsoft 365 plan, and Microsoft does not publish a public per-user list price for GCC High; it is quoted through a Microsoft agreement or an authorized partner.
- GCC High licensing channel: Microsoft sells GCC High through Enterprise Agreement licensing solution providers or, under 500 seats, Authorized Office 365 Supplier for Government (AOS-G) partners. Eligibility validation can start with your Microsoft account team or preferred partner.
- Significant service limitations: External sharing restrictions, broken OneDrive links, Teams chat history limitations, and no PSTN Calling or PSTN Conferencing (Phone System is delivered via Direct Routing) require workflow adjustments and alternative solutions.
- Compliance implementation required: GCC High provides the infrastructure foundation for compliance but requires active configuration of security controls, audit logging, and governance processes to achieve CMMC compliance.
Quick Answer for IT Leaders
A GCC High migration requires a complete tenant rebuild, not an upgrade, with 12-18 month implementation timelines for defense contractors. The process runs through an Enterprise Agreement licensing solution provider or an AOS-G partner, carries a licensing premium over commercial Microsoft 365 that Microsoft does not publish as a public per-user list price, and includes significant service limitations like restricted external sharing and broken OneDrive links. Organizations must plan for $50,000-$200,000 implementation costs while addressing CMMC compliance requirements and workflow disruptions from GCC High’s isolated government cloud architecture.
A Microsoft 365 GCC High migration requires a complete tenant rebuild, not an upgrade. Defense contractors and regulated enterprises should plan for 12 to 18 months from initial assessment to post-migration governance, depending on Active Directory complexity and data volume. Unlike commercial Microsoft 365 migrations, GCC High migration demands specialized services from partners who understand the isolated government cloud architecture and compliance frameworks.
The financial impact extends beyond licensing premiums. GCC High carries a licensing premium over Commercial Microsoft 365, and Microsoft does not publish a public per-user list price for GCC High (it is sold through Microsoft agreements and authorized partners). Implementation costs for organizations with 50-500 users typically range from $50,000 to $200,000, including data migration, identity reconfiguration, and compliance validation. Organizations must also account for service limitations: external sharing is restricted to GCC High-to-GCC High tenants only, OneDrive sharing links from commercial tenants break permanently during migration, and Teams chat history migrates as static HTML files only.
CMMC Level 2 compliance requires all 110 security requirements of NIST SP 800-171 Revision 2, the revision 32 CFR part 170 incorporates by reference. NIST has since published Revision 3, but Revision 3 is not the revision CMMC assesses against. Level 3 adds the enhanced requirements from NIST SP 800-172 for the highest-risk Controlled Unclassified Information. CMMC does not cover classified information at any level. The GCC High migration timeline must align with your CMMC assessment schedule and contract requirements. Organizations that underestimate the complexity or attempt to manage the migration with commercial Microsoft partners face significant delays, cost overruns, and compliance gaps that can jeopardize federal contracting eligibility.
GCC High Migration: Pre-Migration Considerations and Compliance Requirements
Licensing Eligibility and Vetting
Microsoft requires eligibility validation before provisioning GCC High tenants. Defense contractors must demonstrate a legitimate business need for government cloud services through contracts, subcontracts, or direct federal agency relationships. The vetting process includes verification of U.S. citizenship for administrative personnel and confirmation that your organization handles Controlled Unclassified Information (CUI) or Federal Contract Information (FCI).
Eligibility validation typically takes 2-4 weeks but can extend to 8-12 weeks if documentation is incomplete or if Microsoft requires additional verification. Organizations should initiate this process early in their planning timeline. The approval covers the organization, not individual users – but administrative access requires U.S. citizen verification for personnel who will manage the GCC High environment.
Understand Identity and Azure AD Differences
GCC High operates on a completely separate Azure Active Directory infrastructure from commercial Microsoft 365. Your existing Azure AD Connect configuration, custom applications, and third-party integrations that rely on commercial Azure AD endpoints will not function in the GCC High environment. Identity synchronization must be reconfigured to point to GCC High-specific endpoints.
Multi-factor authentication policies, conditional access rules, and device compliance policies require complete reconfiguration. Organizations with complex Active Directory forests or multiple domains face additional complexity in identity architecture planning. The identity migration strategy directly impacts user authentication, device enrollment, and application access during and after the GCC High migration.
Third-Party App Compatibility
Many third-party applications that integrate with commercial Microsoft 365 do not support GCC High endpoints. Software vendors must specifically develop and certify their applications for the government cloud environment. Common business applications – including CRM systems, project management tools, and document management platforms – may require alternative solutions or custom integration work.
Conduct a comprehensive application inventory early in the planning process. Identify applications that access Microsoft Graph API, use OAuth authentication with Microsoft services, or rely on SharePoint or Teams integration. Contact vendors to confirm GCC High support and obtain updated connection strings or configuration guidance. Budget for application replacement or custom development where GCC High support is unavailable.
Single-Event vs. Phased GCC High Migration: Which Approach Fits Your Environment?
Single-event migrations minimize user confusion and reduce the complexity of maintaining parallel environments, but they require extensive preparation and create higher risk if issues arise during cutover. Organizations with fewer than 200 users and straightforward Active Directory configurations often benefit from single-event approaches.
Phased migrations allow for testing and validation at each stage but require careful planning to maintain data consistency and user access across environments. Large organizations or those with complex SharePoint architectures typically require phased approaches. The GCC High migration strategy must account for interdependencies between Exchange, SharePoint, OneDrive, and Teams data, as well as the impact on business processes that span multiple workloads.
Set a Communication Plan
User communication becomes critical when familiar workflows and sharing patterns will change permanently. External sharing restrictions mean that collaboration with partners, vendors, or customers using commercial Microsoft 365 tenants will require alternative methods. OneDrive sharing links that users have distributed will break permanently, and Teams chat history will lose searchability.
Develop role-specific communication plans that address the business impact, not just the technical changes. Project managers need to understand how document sharing with external partners will change. Sales teams need alternative methods for sharing proposals with commercial prospects. IT helpdesk staff need scripts for common user questions about broken links and missing functionality.
GCC High Migration Cost: Licensing, Implementation, and Total Budget Planning
Microsoft 365 GCC High Licensing: G3 vs G5 – Which License Does Your Organization Need?
GCC High carries a licensing premium over Commercial Microsoft 365, and Microsoft does not publish a public per-user list price for GCC High (it is sold through Microsoft agreements and authorized partners). The practical choice is about capability tier, not rate card: G3 covers baseline CMMC Level 2 environments, while G5 adds advanced threat protection, Teams and endpoint data loss prevention, and compliance tools essential for CMMC Level 3 environments.
The licensing decision depends on compliance scope rather than user productivity needs. Budget for the higher tier if your contract portfolio includes any classified work – downgrading licenses after a GCC High migration is administratively complex. An AOS-G partner conducts a compliance assessment to determine which tier your organization requires. Choosing incorrectly costs either contract eligibility (under-licensed) or unnecessary spend (over-licensed).
| License | Cost & Premium | Best For |
|---|---|---|
| GCC High G3 | Not publicly listed; quoted via Microsoft agreement or partner | CMMC Level 2 environments. Includes Exchange Online, SharePoint, OneDrive, Teams (limited), basic security controls. |
| GCC High G5 | Not publicly listed; quoted via Microsoft agreement or partner | CMMC Level 3, ITAR, active audit requirements. Adds advanced threat protection, Teams and endpoint DLP, eDiscovery, Defender, Power BI Pro. |
GCC High Migration ROI: Break-Even for Defense Contractors
GCC High migration ROI calculations differ fundamentally from commercial cloud business cases. The primary driver is contract eligibility, not operational efficiency. Organizations that cannot demonstrate CMMC compliance face contract exclusion as DoD compliance clauses are actively enforced, making the migration a revenue protection investment rather than a cost optimization initiative.
Implementation costs for 50-500 user organizations range from $50,000 to $200,000, including data migration, identity reconfiguration, and compliance validation. Defense contractors should frame ROI around contract risk mitigation: What percentage of your contract pipeline requires CMMC compliance? Organizations with 60%+ CMMC-dependent revenue justify GCC High migration costs within the first contract cycle.
What belongs in a migration project plan for moving from Microsoft 365 Commercial to GCC High for a defense contractor pursuing CMMC Level 2?
Plan the move from Microsoft 365 Commercial to GCC High as a complete tenant rebuild rather than an upgrade, in six phases in order: assessment and compliance gap analysis, Microsoft eligibility validation and licensing, identity architecture, data migration, testing and security baseline, and go-live with post-migration governance. How long that sequence runs, from assessment through post-migration governance, depends on how complex the Active Directory is and how much data moves.
Each phase puts something specific into the plan. Phase 1 gives assessment its own window, longer where identity configurations are complex, and SSP and POA&M documentation starts there. Phase 2 puts licensing procurement after eligibility approval, with tenant provisioning coordinated through an AOS-G partner. Phase 3 pilots the new identity setup with a small user group well ahead of full migration. Phase 4 typically moves Exchange first, SharePoint and OneDrive next, and Teams workspaces last. Phase 5 builds the CMMC controls into the security baseline and checks compliance posture before production, because GCC High supplies the infrastructure foundation while audit logging, security controls, and governance processes still have to be configured to reach CMMC compliance. Phase 6 keeps governance running after migration: access reviews, configuration management, and ongoing security monitoring.
Tenant provisioning is a separate role that an AOS-G partner performs. i3solutions installs and helps configure applications inside IL4 and IL6 government cloud environments and other government networks.
GCC High Migration Process: The 6 Phases of an Enterprise Implementation
Phase 1 – GCC High Migration Assessment and Compliance Gap Analysis
The assessment phase determines how much remediation is required before data moves. It maps existing Microsoft 365 configurations against GCC High constraints and CMMC requirements, including Active Directory architecture review, third-party application inventory, data classification analysis, and compliance gap identification. Organizations should allocate 4-6 weeks for comprehensive assessment in environments with complex identity configurations.
Document every SharePoint site, Teams workspace, Power Platform solution, and external sharing relationship. GCC High’s isolation requirements break many existing workflows, and the assessment phase identifies which processes require redesign versus direct migration. SSP and POA&M documentation begins here. The assessment deliverable becomes the foundation for migration planning and budget validation.
Phase 2 – Microsoft Eligibility Validation and GCC High Licensing
Microsoft’s eligibility verification process requires documentation of government contracts, facility security clearances, and defense industrial base participation. The validation typically takes 30-60 days and determines which GCC High services are available to your organization. Some advanced compliance features require additional clearance levels beyond basic contractor status.
Licensing procurement follows eligibility approval and runs through an AOS-G partner or, at 500 seats and up, an Enterprise Agreement licensing solution provider. Volume licensing eliminates trial options – license commitment is required upfront, making partner selection a critical risk decision before this phase begins. Organizations should secure licensing commitments before detailed GCC High migration planning begins, as license availability and pricing can change based on government procurement cycles.
Phase 3 – Identity Architecture and Access Strategy
Identity migration requires complete Azure Active Directory reconfiguration to GCC High endpoints. Existing federated identity configurations, conditional access policies, and multi-factor authentication settings must be rebuilt from scratch. Organizations using ADFS or Azure AD Connect need identity synchronization reconfiguration – including objectSID alignment and domain cutover coordination – with extensive testing before production cutover.
Plan for identity pilot testing with a small user group at least 60 days before full migration. Complex Active Directory environments with multiple forests, custom attributes, or legacy authentication methods often become the critical path constraint for the entire GCC High migration timeline. Conditional Access and SSO configurations should be validated against GCC High policy templates before any production users migrate.
Phase 4 – Data Migration: Exchange, SharePoint, OneDrive, and Teams
Data migration requires specialized tools that support GCC High endpoints – standard Microsoft migration utilities do not work across the commercial-to-government boundary. Exchange migration typically proceeds first, followed by SharePoint and OneDrive, then Teams workspaces. Each workload carries specific limitations that must be planned before the GCC High migration begins.
- Exchange: Mailbox migration proceeds with tools certified for GCC High endpoints. Mail flow rules and transport configurations require reconfiguration in the destination tenant.
- SharePoint and OneDrive: Document library structures, metadata, and permissions transfer correctly. OneDrive sharing links from the source commercial tenant break permanently during migration and cannot be restored in the GCC High environment.
- Teams: Chat history migrates as static HTML files only – losing searchability and the interactive features users rely on for project continuity. Organizations dependent on Teams chat for project documentation should implement alternative record-keeping strategies before migration.
Plan for data validation testing at each workload migration to ensure business-critical information transfers correctly and maintains required compliance controls.
Phase 5 – Testing, Validation, and Security Baseline Configuration
Security baseline configuration implements CMMC controls and validates compliance posture before production use. This phase includes conditional access policy deployment, data loss prevention rule configuration, and security monitoring setup. CMMC Level 2 requires all 110 security requirements of NIST SP 800-171 Revision 2. Level 3 adds the enhanced security requirements selected from NIST SP 800-172, and it applies to the highest-risk Controlled Unclassified Information, not to classified information. These configurations are mandatory at this phase – not optional post-migration adjustments.
User acceptance testing focuses on workflow validation rather than feature testing. The core Microsoft 365 functionality remains consistent, but sharing restrictions and integration limitations require process adjustments. Plan for at least 2-3 weeks of security validation and user workflow testing before go-live authorization.
Phase 6 – Go-Live, User Adoption, and Post-Migration Governance
Go-live coordination includes device re-enrollment, user communication, and support desk preparation for GCC High-specific limitations. External sharing restrictions and broken integration workflows generate the highest volume of user support requests during the first 30 days post-migration. Prepare helpdesk scripts for these known issues before cutover.
Post-migration governance focuses on maintaining CMMC compliance through ongoing security monitoring, access reviews, and configuration management. Organizations must establish governance procedures for new application onboarding, user provisioning, and external collaboration requests within GCC High constraints. Audit readiness reviews and security baseline validation should be scheduled before your first DoD audit cycle.
GCC High Migration Project Plan: Nine Stages, Named Owners, and Four Signed Gates
The six phases above say what has to happen. A plan that survives an assessor also says who owns each step, what condition opens it, what artifact closes it, and who signs the go or no-go between them. Broken out at that level, the six phases become nine stages. Each stage produces a deliverable your C3PAO assessor will ask for anyway, so the migration plan and the evidence package end up as the same document.
The nine stages, with owners, entry conditions and exit artifacts
The “starts when” column carries entry conditions rather than dates. Eligibility validation finishes on Microsoft’s schedule, not yours, so express the sequence in conditions and attach dates to stage 4 onward once Microsoft returns eligibility.
| Stage | Owner | Starts when | Closes on |
|---|---|---|---|
| 1. Eligibility validation and licensing channel | Contracts lead | Day one, unconditionally | Validated eligibility and provisioned tenant |
| 2. Estate inventory and disposition register | IT Director | Day one, in parallel | Disposition register, one decision per object |
| 3. Feature adjudication | Enterprise architect | Estate inventory has a first pass | Feature gap register with a business owner per gap |
| 4. Identity architecture and network allow list | Identity engineer | Tenant provisioned (stage 1 closed) | Directory live, sync reconfigured, allow list deployed |
| 5. Security baseline and evidence instrumentation | ISSM | Directory live | Baseline applied and audit collection running |
| 6. Cross cloud coexistence | Identity engineer and collaboration lead | Baseline applied | Verified collaboration between both tenants |
| 7. Waved data migration | Migration lead | Ready-to-move gate signed | Last wave reconciled |
| 8. Cutover, decommission and support handling | IT Director and ISSM | Last wave reconciled | Commercial tenant retired to a documented state |
| 9. Evidence package and standing governance | ISSM and records manager | Stage 5 output exists | Assessment ready package under version control |
Three of these stages carry decisions that most plans skip.
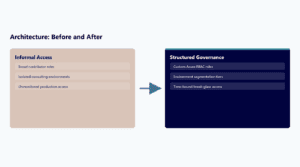
Stage 2, the disposition register. One register, one decision per object, four permitted values: migrate, rebuild, retire, leave in commercial. The fourth value is not a failure state. It is often the correct architecture, and it is why this stage runs in parallel with stage 1 rather than after it. Inventory exhaustively, for a reason i3solutions attests from its own delivery work rather than from a market statistic: “Lift-and-shift migrations typically carry over 60 to 80% of existing permission inconsistencies, creating immediate audit exposure in Microsoft 365 environments rather than resolving the underlying governance debt.” Every permission has to be reissued in the new tenant anyway, so remediation during the register is a decision about what to reissue, not a separate project with its own funding. The register closes when application owners sign it, not IT alone.
Stage 5, evidence instrumentation before wave 1. Audit records exist only from the moment collection is switched on, and nothing generates them retroactively. Migration is also the window in which privileged access is at its broadest: temporary administrative roles are granted for the duration, and the third party migration accounts hold high privilege in both tenants at once. An assessor will ask how that access was controlled, so switch collection on before the first user moves, not after go-live. The i3solutions Federal Compliance Assessment evaluates a client tenant against NIST SP 800-53 and CMMC using automated tenant configuration scripts and a 42-point security checklist. Run an assessment of that kind against the new tenant while it is still empty, and every finding is a configuration change on its own rather than a configuration change plus a data migration to carry it.
Stage 7, waved migration. Wave by business boundary, not by alphabet: a wave should be a group of people who mostly work with each other, so the coexistence gap sits between waves rather than through the middle of a program team. Per wave, plan a content freeze window with a named approver, a permissions reconciliation step run after the copy rather than trusting the tool’s report, a rollback condition stated before the wave opens, and a delta pass for anything created during the freeze. A published example of a migration run under continuity-of-operations pressure is the Cloud Migration and Continuity of Operations case study.
The critical path, and the three dependencies that reorder it
The critical path runs stage 1 to stage 4 to stage 5 to stage 6 to stage 7 to stage 8. Stages 2 and 3, the estate inventory and the feature adjudication, run in parallel and feed stage 7. Stage 9 accumulates continuously.
- Eligibility validation finishes on Microsoft’s schedule. It is the only stage whose finish date you do not control, so it starts first and every downstream date is expressed relative to it rather than to a calendar.
- Evidence collection precedes wave 1. Instrumenting after go-live cannot be retrofitted, because the window you lost is the migration itself.
- Cross cloud collaboration precedes wave 1. Configure it while nobody depends on it. If the first wave discovers it, you have already spent the credibility you needed for every wave that follows.
Who owns what on your side
| Role | Accountable for | The decision only they can make |
|---|---|---|
| Contracts lead | Stage 1 | Which contract clauses and CUI categories set the scope |
| IT Director | Stages 2 and 8, and the schedule | Wave sequencing and the decommission state |
| Enterprise architect | Stage 3 | What stays in the commercial tenant |
| Identity engineer | Stages 4 and 6 | Synchronization topology and the credential model |
| ISSM | Stages 5, 8 and 9 | Whether evidence is sufficient to open a wave |
| Records manager | Stage 9, and retention input to stage 2 | What is retained and for how long |
| Application owners | Their rows in the disposition register | Migrate, rebuild, retire, or leave |
| Facility security officer | Access review across stages 4 and 6 | Who may hold access in the new tenant |
The four gates, and who signs them
- Scope committed. Signed by the contracts lead and the ISSM. Evidence: the CUI scope determination and the disposition register. No licensing commitment before this.
- Environment fit accepted. Signed by the enterprise architect and the business sponsor. Evidence: the feature gap register, every row owned and decided. This is the last cheap moment to change the target.
- Ready to move people. Signed by the ISSM. Evidence: baseline applied, audit collection dated before this signature, cross cloud collaboration verified against a real user in each tenant. This is the gate worth defending, because it is the only one whose absence stays invisible until an assessor asks.
- Ready to decommission. Signed by the IT Director and the records manager. Evidence: all waves reconciled, retention and export decisions executed, support handling procedure trained.
Running the plan in-house or with an integrator
Either way, the stage table is the contract. If an integrator runs part of the plan, name the stages it owns and the exit artifacts it hands back signed. A proposal that cannot be mapped onto those stages is a different plan, and its gaps sit in the stages nobody named.
Microsoft applies its own personnel controls on the platform side. Its GCC High and DoD service description lists U.S. citizenship verification, seven year employment and criminal history checks, and validation against the Treasury OFAC, Commerce BIS and State DDTC lists for any staff granted temporary elevated access to GCC High customer content. Your integrator should be able to describe an equivalent standard for its own engineers without being asked twice.
For context on the firm that wrote this plan: i3solutions has been a Microsoft partner since 1997 and has delivered 600+ implementations across aerospace and defense, financial services, and health sciences. i3solutions has deployed Power BI inside a GCC High tenant and inside Azure Government for a federal customer. i3solutions runs a governed Power Platform for a federal defense agency supporting roughly 10,000 personnel across about 180 locations, which works because it is governed, not despite it.
GCC High Service Limitations and Architecture Constraints Your Team Must Plan Around
GCC High operates with significant service limitations that require workflow adjustments and alternative solutions. External sharing is restricted to GCC High-to-GCC High tenants only, breaking existing partner collaboration workflows that rely on commercial tenant sharing. Organizations accustomed to sharing documents with commercial partners, suppliers, or subcontractors must establish alternative file exchange mechanisms.
PSTN Calling and PSTN Conferencing are not available in GCC High, and Teams Phone System is delivered via Direct Routing, requiring a Direct Routing deployment for organizations dependent on integrated calling features. Teams functionality is further limited: guest access is restricted to other government tenants, and many third-party Teams applications do not support GCC High endpoints.
Power Platform capabilities are reduced in GCC High environments. Many premium connectors for commercial SaaS applications are unavailable, and custom connector development faces additional security review requirements. Organizations with extensive Power Platform automation should inventory existing flows and plan for alternative solutions where connectors are unsupported.
SharePoint migration tools face compatibility constraints – popular third-party migration utilities may not support GCC High endpoints, requiring manual migration processes or specialized tooling. Document library structures, metadata, and permissions transfer correctly, but workflow automation and custom solutions often require redevelopment for GCC High compatibility.
How Microsoft 365 Updates Reach GCC High, and How to Track Them
Microsoft states that feature availability may differ across its government clouds and that release timing typically lags behind the commercial environment, so a commercial announcement date is not a GCC High date. Track it from inside your own tenant instead: Message center shows each announced feature’s release status for your organization as Scheduled, Rolling out, or Launched, for any feature that is also listed on the Microsoft 365 Public Roadmap. Carry that status into the same service-availability record your migration plan already keeps for confirmed features, rather than treating a commercial rollout announcement as an assumption you can plan around.
Why GCC High Migrations Fail – and What a Qualified Partner Prevents
Blocked or Unsupported Third-Party Integrations
Third-party application failures represent the most common cause of GCC High migration delays and budget overruns. Applications that integrate seamlessly with commercial Microsoft 365 often lack government cloud compatibility, forcing organizations to discover these limitations during implementation rather than planning phases.
Document management systems, workflow automation tools, and collaboration platforms frequently use Microsoft Graph API endpoints that require reconfiguration for government cloud infrastructure (graph.microsoft.us instead of graph.microsoft.com). Some vendors offer separate GCC High-compatible versions at premium pricing, while others provide no government cloud support at all – forcing application replacement decisions during active migration projects.
Delays in Licensing Approval
Microsoft’s eligibility validation process creates unpredictable project delays when organizations lack proper documentation or submit incomplete applications. The standard 30-60 day validation timeline extends significantly for organizations without readily accessible CAGE codes, contract excerpts showing DFARS 252.204-7012 requirements, or clear CUI handling documentation.
Organizations frequently underestimate the documentation requirements for eligibility validation. Microsoft may request additional contract details, organizational structure information, or clarification on government relationships during the review process. Each documentation request adds 2-3 weeks to the validation timeline, cascading delays through the entire GCC High migration schedule.
Identity Synchronization Failures
Identity architecture rebuild failures occur when organizations attempt to replicate their commercial Azure AD configuration without accounting for government cloud constraints. Conditional access policies, device compliance settings, and multi-factor authentication configurations must be rebuilt from scratch using GCC High policy templates that may not support all commercial tenant features.
Device re-enrollment presents coordination challenges that affect every user simultaneously. Windows devices joined to commercial Azure AD domains require disjoin and re-enrollment procedures that can fail if not executed in proper sequence. Mobile device management policies need reconfiguration against government cloud endpoints, potentially leaving devices unmanaged during transition periods.
Compliance Blind Spots
Organizations frequently assume that GCC High migration automatically achieves CMMC compliance without implementing required security controls and governance processes. GCC High provides the infrastructure foundation for compliance but requires configuration of data loss prevention policies, audit logging, insider risk management, and access controls that align with NIST 800-171 requirements.
Audit logging configuration errors create compliance gaps that become apparent during CMMC assessments. Organizations must implement specific logging retention periods, event monitoring, and access review processes that exceed GCC High default configurations. Missing or misconfigured audit controls can result in CMMC assessment failures despite a successful technical GCC High migration.
Device Re-enrollment and Endpoint Disruption
Device management disruption affects user productivity more severely than organizations anticipate. Windows devices require complete disjoin from commercial Azure AD and re-enrollment to GCC High tenants, creating periods where devices lack policy enforcement or security monitoring. This process cannot be automated and requires user coordination for each affected device.
Endpoint protection solutions may require reconfiguration or replacement to support GCC High infrastructure. Some security tools lack government cloud compatibility, creating security gaps during transition periods. Organizations must plan for alternative endpoint protection or accept temporary security posture reductions while implementing compatible solutions.
Choosing the Right GCC High Migration Partner: What to Evaluate Beyond Price
What Is an AOS-G Partner and When Do You Need One for GCC High Migration?
AOS-G (Authorized Office 365 Supplier for Government) partners are Microsoft’s GCC High licensing channel for organizations under 500 seats; at 500 seats and up, licensing solution providers transact it through an Enterprise Agreement. Microsoft says eligibility validation can start with your account team or preferred partner, so AOS-G credentials matter for the license order under 500 seats, not for every firm on the project.
AOS-G partners undergo background investigations and maintain compliance certifications that enable them to handle CUI and support government cloud environments. This vetting process includes security clearance requirements for key personnel, facility security measures, and ongoing compliance monitoring that standard Microsoft partners do not maintain.
The licensing channel affects project timelines and vendor selection decisions. Organizations that select a non-AOS-G implementation partner still need an AOS-G partner or licensing solution provider for the license order, so name both roles early to avoid project delays, knowledge transfer requirements, and potential cost increases. Verify AOS-G status during initial vendor evaluation rather than discovering this requirement during implementation planning. Apply the same timing to the platform side of the engagement: the criteria used to hire a GCC High implementation firm belong in the evaluation stage, before a tenant is committed.
What i3solutions Delivers for Your GCC High Migration
i3solutions is a Microsoft partner, not an AOS-G supplier. AOS-G tenant provisioning is a separate role that a certified AOS-G supplier performs, and i3solutions works alongside that supplier rather than in place of it. What i3solutions brings is platform depth: we work inside IL4, IL6, and other government networks, installing and configuring applications there, paired with defense contractor compliance requirements and Microsoft government cloud architecture. Our team understands both CMMC implementation requirements and GCC High technical constraints, enabling integrated planning that addresses compliance and technical migration simultaneously.
Our approach includes pre-migration compliance gap analysis, NIST 800-171 control implementation, and CMMC assessment preparation that generic Microsoft partners cannot provide. We document security control implementation evidence and audit trail requirements that support your CMMC certification process.
The architectural planning process accounts for GCC High’s service limitations and integration constraints from project initiation – not during implementation. Our documentation – SOW, architecture diagrams, compliance mapping, decision gates – gives your IT Director or CTO a defensible paper trail for internal stakeholders, procurement, and auditors. You need a record of governed decisions, not just a completed GCC High migration.
GCC High Migration Partner Evaluation Criteria
Essential Qualifications to Verify Before Vendor Selection
- AOS-G Partnership Status: Confirm current Authorized Office 365 Supplier for Government credentials through Microsoft’s partner directory. Under 500 seats, GCC High licenses come from an AOS-G partner; at 500 seats and up, from an Enterprise Agreement licensing solution provider.
- Government Cloud Experience: Request specific case studies from defense contractors or regulated enterprises with similar compliance requirements (CMMC, ITAR, FedRAMP). Generic Microsoft 365 experience does not translate to GCC High migration expertise.
- CMMC Implementation Capability: Verify the partner can implement NIST 800-171 security controls and provide audit-ready documentation for CMMC assessments. Many Microsoft partners lack compliance implementation expertise.
- Identity Architecture Expertise: Confirm experience with Azure AD reconfiguration for government cloud endpoints, including ADFS integration, conditional access policies, and device management in isolated environments.
- Third-Party Integration Assessment: Ensure the partner conducts comprehensive application compatibility analysis before migration begins. Discovering integration failures during implementation causes significant delays and cost overruns.
Red Flags That Predict GCC High Migration Project Failure
- Partners who claim GCC High migration is “just like commercial” – this indicates lack of government cloud experience.
- Vendors without current AOS-G credentials who promise to “get certified during the project.”
- Proposals that don’t address service limitations: external sharing restrictions, Teams functionality, Power Platform constraints.
- Fixed-price quotes without a detailed application inventory and compatibility assessment.
- Partners who cannot provide specific CMMC implementation experience and audit trail documentation.
GCC High Migration Budget Planning Framework
Cost Categories for Accurate Budget Development
- Licensing Premium: Budget for a premium over commercial Microsoft 365. Microsoft does not publish a public per-user list price for GCC High, so get a quote through your Microsoft agreement or an authorized partner rather than budgeting from a public rate.
- Implementation Services: Professional services typically range $50,000-$200,000 for 50-500 user organizations, including assessment, migration, and compliance configuration.
- Third-Party Application Costs: Budget for application replacement or custom integration where GCC High compatibility is unavailable. Common cost drivers include CRM systems, workflow automation, and document management platforms.
- Training and Change Management: User productivity impact from service limitations requires structured training programs and workflow redesign.
- Ongoing Compliance Maintenance: Post-migration governance, security monitoring, and audit preparation require dedicated resources or managed services.
GCC High Migration Timeline and Budget Allocation
| Phase | Timeline | Budget & Key Activities |
|---|---|---|
| Assessment & Planning | Months 1-3 | 20% of budget – Compliance gap analysis, application inventory, eligibility validation |
| Identity & Data Migration | Months 4-8 | 50% of budget – Azure AD reconfiguration, workload migration, integration remediation |
| Testing & Go-Live | Months 9-12 | 20% of budget – Security baseline, user acceptance testing, cutover coordination |
| Post-Migration Governance | Months 13-18 | 10% of budget – Audit readiness, compliance monitoring, access reviews |
ROI Calculation Framework
Defense contractors should evaluate GCC High migration as contract risk mitigation rather than operational efficiency. Calculate the percentage of your contract pipeline requiring CMMC compliance and compare potential revenue loss from non-compliance against migration costs. Organizations with 60%+ CMMC-dependent revenue typically justify GCC High migration costs within the first contract cycle.
Frequently Asked Questions: GCC High Migration for Defense Contractors
How long does a complete GCC High migration take for a mid-sized defense contractor?
A complete GCC High migration requires 12-18 months from initial assessment to post-migration governance for organizations with complex Active Directory environments and extensive third-party integrations. Organizations with fewer than 100 users and standardized configurations can complete migration in 6-9 months, while larger organizations with custom SharePoint solutions or numerous line-of-business integrations require longer timelines.
What is the total cost difference between GCC High and commercial Microsoft 365 for a 200-user organization?
GCC High carries a licensing premium over Commercial Microsoft 365, and Microsoft does not publish a public per-user list price for GCC High (it is sold through Microsoft agreements and authorized partners). Model the licensing line item from your own seat count and your actual quoted rate, because the delta cannot be derived from published pricing. Implementation costs for a GCC High migration typically range from $75,000-$150,000 for this organization size, including data migration and compliance configuration.
Can we maintain external sharing with commercial Microsoft 365 users after migrating to GCC High?
No. External sharing in GCC High is restricted to GCC High-to-GCC High tenants only. Existing sharing links to commercial Microsoft 365 users break permanently during migration and cannot be restored. Organizations must establish alternative collaboration methods or require external partners to obtain GCC High tenants for continued document sharing.
What happens to our Teams chat history during GCC High migration?
Teams chat history migrates as static HTML files that lose searchability and interactive features. Users cannot search historical conversations or access embedded files through migrated chat records. Organizations dependent on Teams chat for project documentation should implement alternative record-keeping strategies before the GCC High migration begins.
When is AOS-G partnership status required for GCC High implementations?
Microsoft sells GCC High through AOS-G (Authorized Office 365 Supplier for Government) partners for organizations under 500 seats, and through Enterprise Agreement licensing solution providers at 500 seats and up. Eligibility validation can start with your Microsoft account team or preferred partner. AOS-G partners maintain security clearances and compliance certifications required for government cloud environments.
How long does Microsoft’s eligibility validation process take for GCC High?
Eligibility validation typically takes 30-60 days but can extend to 8-12 weeks if documentation is incomplete. Organizations need government contracts, CAGE codes, and CUI handling documentation readily available. Each additional information request from Microsoft adds 2-3 weeks to the GCC High migration timeline – factor a minimum 60-day buffer into any contract-aligned deadline.
What third-party applications stop working after GCC High migration?
Many applications using Microsoft Graph API, OAuth authentication with Microsoft services, or SharePoint and Teams integration require GCC High-specific versions or complete replacement. Common issues include CRM systems, project management tools, and workflow automation platforms that lack government cloud compatibility. Conduct a full application inventory and vendor compatibility audit before the GCC High migration begins, not after.
Do Microsoft 365 updates reach GCC High at the same time as commercial?
No. Microsoft states that feature availability may differ in the government clouds and that release timing typically lags behind commercial, so a feature announced or launched commercially is not confirmed for GCC High until your tenant’s Message center shows it as Scheduled, Rolling out, or Launched for your organization.
Does GCC High migration automatically make us CMMC compliant?
No. GCC High provides the infrastructure foundation but requires active configuration of security controls, audit logging, and governance processes. CMMC Level 2 requires implementing all 110 NIST SP 800-171 Revision 2 security requirements beyond basic GCC High setup. Level 3 adds the NIST SP 800-172 enhanced requirements on top of a Level 2 certification. Compliance is achieved through configuration and governance – not GCC High migration alone.
What is the biggest risk factor for GCC High migration project failure?
Third-party application compatibility issues cause the most delays and budget overruns in a GCC High migration. Organizations often discover integration failures during implementation rather than planning phases, requiring application replacement or custom development that extends timelines and increases costs significantly. A comprehensive pre-migration application inventory is the single most effective risk mitigation step.
Can we convert our existing commercial tenant to GCC High instead of building a new one?
Microsoft does not document a conversion path, and in its cross-tenant mailbox migration documentation it documents the absence of a migration path between clouds: “Cross cloud tenant to tenant migration isn’t supported. An example scenario would be moving from Office 365 Worldwide to Office 365 Government Cloud.” Plan for a separate tenant, a coexistence period, and third party migration software. Anyone quoting you an in-place upgrade should be asked to point at the Microsoft documentation for it.
When should we hold off on starting a GCC High migration plan?
When any of four things is true. Your CUI scope determination is not written and signed, so the first stage has no valid entry condition and you would be buying an environment on an assumption. Nobody has tested whether GCC is sufficient: the feature losses in GCC High are real and permanent, and if GCC meets your obligations the correct plan is a different and much shorter one. You have not priced the partial option: moving only the workloads that hold CUI is a legitimate architecture, and the disposition register is where you find out whether it applies to you. Or you need an end date before Microsoft returns eligibility: you can commit to a sequence now, but an end date set before that answer arrives rests on the one step you do not control.
External Citations and Sources
Government and Compliance Sources
- NIST Special Publication 800-171 Rev. 3 – Protecting Controlled Unclassified Information in Nonfederal Systems and Organizations
- CMMC Model Overview – Department of Defense Cybersecurity Maturity Model Certification requirements and assessment procedures
- Microsoft GCC High and DoD Service Description – Official Microsoft documentation of GCC High capabilities and limitations
Industry Analysis and Research
- Gartner Magic Quadrant for Cloud Infrastructure and Platform Services – Enterprise cloud adoption trends and vendor evaluation criteria
- Forrester Wave: Enterprise Email Security – Security requirements for regulated industries and government contractors
Technical Implementation Guidance
- Microsoft Learn: Microsoft Entra Connect for Government Clouds – Identity synchronization configuration for GCC High environments
- Microsoft Tech Community: Microsoft 365 Government – Community-driven guidance and lessons learned from government cloud implementations
Ensure a Seamless Enterprise GCC High Migration With i3solutions
A GCC High migration is a board-level risk decision for most defense contractors – not a routine IT project. The difference between a migration that protects your compliance posture and one that exposes you to contract risk comes down to architecture decisions made in the first 30 days.
i3solutions provides senior-level, U.S.-based Microsoft expertise for regulated organizations. We manage GCC High migrations end-to-end: from eligibility validation and licensing coordination with your AOS-G supplier through identity architecture, data migration, security baseline configuration, and post-migration governance.
Where GCC High migrations actually stall
A checklist keeps the move honest, but the sequencing, the Entra ID tenant decisions, and the data-boundary calls are where GCC High migrations stall, not the technical lift. Talk to our team about your tenant and compliance obligations before you commit to a cutover date.