
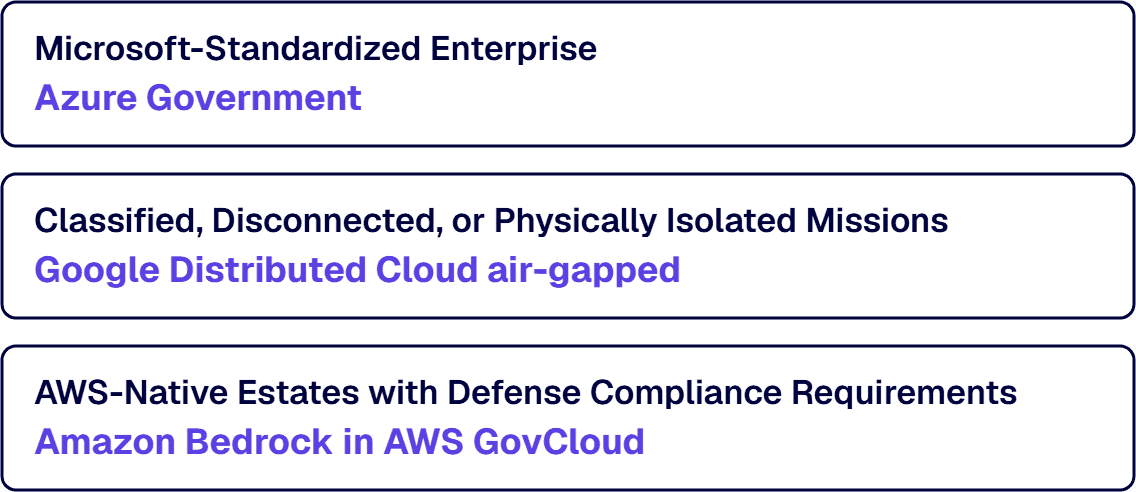
For regulated US organizations standardized on Microsoft 365 and Entra ID, Microsoft offers the strongest hybrid answer today. Azure Government maintains FedRAMP High authorization, and Foundry Local on Azure Local enables inference on Arc-managed Kubernetes clusters within your own infrastructure, keeping both halves in a unified identity plane. For classified or genuinely disconnected missions, Google Distributed Cloud air-gapped is the option designed for that shape; for AWS-native estates with defense compliance, Bedrock in GovCloud with the FedRAMP Class D and DoD IL4/IL5 model list covers the cloud tier and on-premises tiers should be designed separately.
The term “hybrid” encompasses three distinct architectural patterns in regulated contexts, and naming which one a program actually needs is the intervention that removes most disagreement from a vendor comparison.
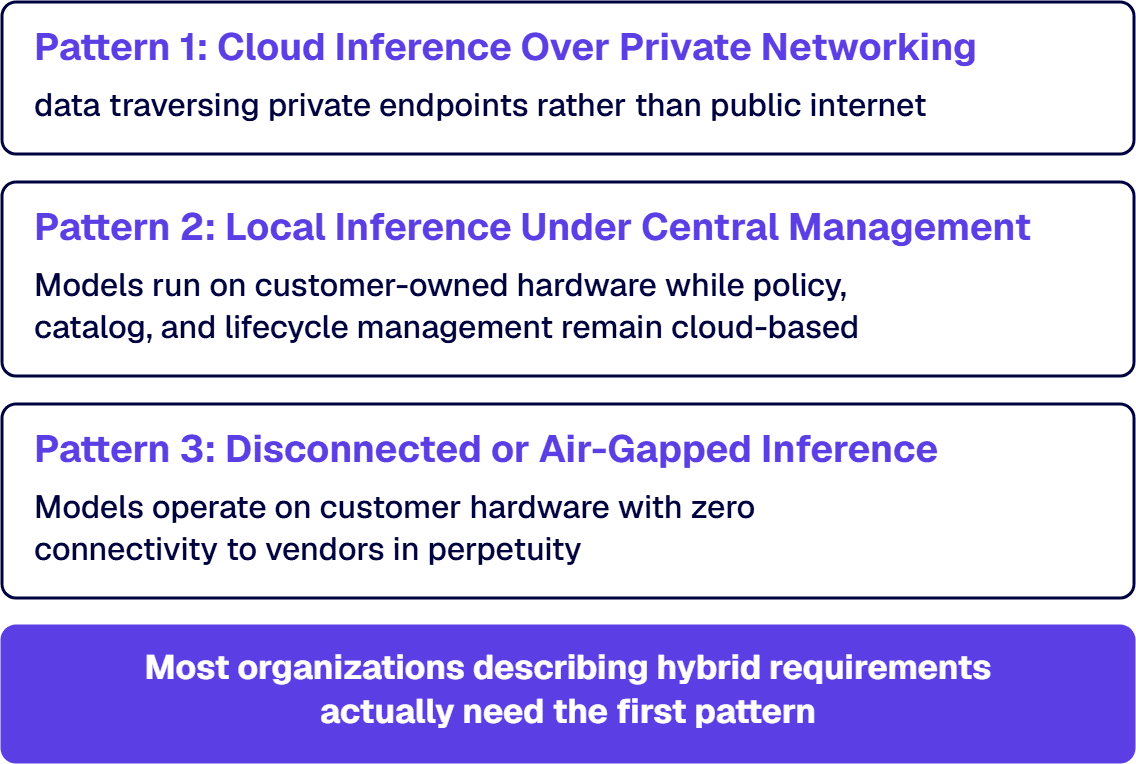
Models operate in accredited cloud regions with data traversing private endpoints rather than public internet, maintaining identity and logging within tenant boundaries. Every major vendor supports this configuration.
Models run on customer-owned hardware while policy, catalog, and lifecycle management remain cloud-based. This satisfies data-residency and latency requirements without sacrificing centralized governance.
Models operate on customer hardware with zero connectivity to vendors in perpetuity. This approach separates vendors significantly, as it demands purpose-built products for operation without external dependencies.
Most organizations describing hybrid requirements actually need the first pattern and can achieve it across any major platform. The architectural distinction, not vendor selection, drives implementation complexity. Establishing which pattern matches your requirement before the platform conversation eliminates most disagreement.
Microsoft’s Azure Government receives FedRAMP High impact level assessment and authorization, with contractual commitments ensuring customer data remains stored in the United States and accessible only to screened US citizens. Foundry Local on Azure Local represents Microsoft’s substantive on-premises offering. The service brings AI inference to your Azure Local environment through deployment on Arc-enabled Kubernetes clusters with Kubernetes-native operations, enabling you to keep your data processing on-premises where your data is generated.
Three capabilities are critical for regulated designs. Inference endpoints employ API keys, Microsoft Entra ID authentication, and TLS-enabled gateway API patterns, maintaining on-premises components within the same identity plane as cloud services. The product operates in disconnected environments where internet connectivity is not available, with the deployment model consistent with connected scenarios. Compliance stands as a primary use case: keep inference and data processing on-premises for sovereignty or regulatory requirements.
The maturity constraint is real. Foundry Local remains in preview status; deployment is currently available by request during preview through access request forms. Its supported-region list names commercial Azure regions exclusively, without US Government regions included. Production regulated workloads should not deploy on preview services with gated deployment paths. Running workloads in Azure Government now, with on-premises inference tiers scheduled as second-phase work contingent on general availability, is the prudent approach.
AWS published clear authorization statements for defense applications. On June 25, 2026, AWS announced that OpenAI GPT, OpenAI GPT OSS, and NVIDIA Nemotron models have FedRAMP High and DoD IL-4/5 approval in AWS GovCloud (US). The Amazon Bedrock certification status page, last updated September 18, 2026, enumerates models carrying FedRAMP Class D and IL4/5 authorization, including Titan Text Embeddings, Claude Sonnet variants, and Llama models.
AWS describes Bedrock as serverless with availability defined by Region. No AWS documentation describes Bedrock inference operating on customer-owned hardware. This represents an absence of documentation rather than explicit prohibition, but designing on-premises infrastructure around undocumented capabilities creates schedule risk without mitigation options.
The service documentation specifies that certain customer-defined metadata may leave the AWS GovCloud (US) Regions only when the customer asks AWS to investigate a reported issue, and model evaluation metadata is not permitted to contain export-controlled data. These constraints prove workable but require early visibility in ITAR reviews.
Google’s documentation builds from the disconnected end rather than the cloud end. Google Distributed Cloud air-gapped lets you host, control, and manage infrastructure and services directly on your premises and does not require connectivity to Google Cloud, helping customers meet compliance and regulatory requirements. Google Cloud’s April 9, 2025 announcement describes GDC as a fully managed on-prem and edge cloud solution offered in both connected and air-gapped options, scaling from a single server to hundreds of racks. The announcement states the air-gapped product carries authorization for US Government Secret and Top Secret missions with Gemini availability.
Gemini for Government deployment requires specific configuration: only models supporting US multi-regional endpoints offer data residency commitments supporting FedRAMP High and DoD IL4/IL5 deployments. Deployment must occur within Assured Workloads folders configured for compliance regimes, with US Multi-region selected as application location. This is a build instruction rather than a default.
Google’s public documentation contains thinner model-by-model authorization detail than Microsoft’s Azure Government material or AWS’s certification lists. Much authoritative evidence resides in announcements rather than reference documentation. When disconnected requirements are genuine, evaluation should proceed as direct engagement with Google under agreement rather than documentation review alone.
| Evaluation Criterion | Microsoft | AWS | |
|---|---|---|---|
| Documented first-party on-premises inference | Yes. Foundry Local on Azure Local via Arc-enabled Kubernetes. Preview and request-gated. | Not found in AWS documentation. Bedrock documented as serverless. Status unresolved. | Yes. Google Distributed Cloud with connected and air-gapped options. Gemini available on air-gapped product. |
| Documented disconnected operation | Yes, listed as Foundry Local capability. Under preview caveats. | Not identified in Bedrock documentation reviewed. | Yes. Design center for GDC air-gapped product; no Google Cloud connectivity requirement. |
| Accredited US public-sector cloud component | Azure Government: FedRAMP High with US-storage and screened-US-persons contractual commitments. | AWS GovCloud (US-West) and (US-East) with named model list at FedRAMP Class D and DoD IL4/IL5. | Google Cloud with Assured Workloads, conditional on US multi-regional endpoints and proper folder configuration. |
| Identity plane spanning both halves | Unified. Microsoft Entra ID authenticates cloud services and on-premises inference endpoints. | AWS IAM handles cloud half. On-premises half undefined; identity story unclear. | Google identity in connected configuration. Air-gapped enclaves operate as independent worlds by design. |
| On-premises option maturity | Preview, deployment by request. Primary risk in the Microsoft recommendation. | Not applicable. | Generally available product line with named public-sector authorizations. |
| Operational model | Inherit cloud accreditation; build and operate the on-premises cluster. | Inherit nearly everything; accept Regional constraints. | Inherit appliance-shaped platform; own the physical enclave around it. |
Data boundaries, sensitivity labels, and per-user auditability are where enterprise AI projects hold or fail. i3solutions’ AI and Copilot specialists are senior-level, 100% US-based, and deliver inside the compliance standards regulated tenants run.
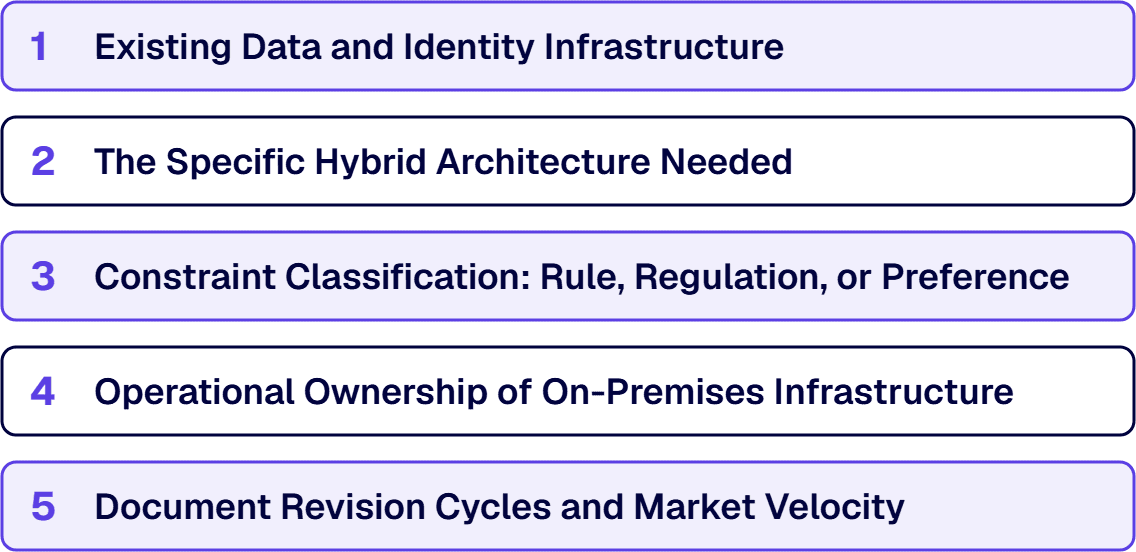
This consideration outranks every model benchmark. Content in SharePoint, users in Entra ID, and DLP policy in Purview means non-Microsoft AI platforms require second identity paths, second logging, and second policy surfaces. Those costs accrue monthly through audit cycles, and they are the reason a Microsoft-standardized enterprise usually lands on Microsoft even when a different model benchmarks higher on paper.
Most organizations describing hybrid requirements need private-network access to cloud inference and can achieve this across all three platforms. A smaller population genuinely requires local inference under central management. Fewer still need air-gapped disconnected operation. Establishing which pattern matches the requirement before the platform conversation eliminates most disagreement.
“Data cannot leave our network” statements may originate from authorizing official controls, pre-FedRAMP internal policies, or intuitive preferences. These carry very different compliance costs. Checking which category applies determines whether buying on-premises infrastructure is justified at all.
Kubernetes clusters with GPU nodes serving production inference require dedicated on-call rotations and infrastructure expertise. If no team exists for this role and none is being hired, hybrid designs chosen for compliance become unmaintainable boundaries, worsening the actual risk posture relative to cloud alternatives.
Every decision-bearing fact on this page comes from vendor documentation revised within the current year, with one option remaining in preview. That market property demands recommendations documented with evidence, revision dates, and scheduled review cycles rather than permanent resolution.
Deploy workloads in Azure Government using Azure OpenAI and AI Search government endpoints, maintaining existing identity and DLP machinery. Introduce on-premises inference tiers only where specific datasets or latency requirements demand it, recognizing Foundry Local on Azure Local preview status. This scenario covers the large majority of regulated US enterprises and wins through unified governance planes rather than AI feature advantages.
Google Distributed Cloud air-gapped is the option whose documentation targets exactly this requirement, with Secret and Top Secret authorization and Gemini available per Google’s April 9, 2025 announcement. This path currently offers the shortest route to market for disconnected requirements. Evaluate directly with Google under agreement.
Amazon Bedrock in AWS GovCloud with the named model list at FedRAMP Class D and DoD IL4/IL5, per AWS’s certification status page, provides strong, dated, specific answers for cloud components. Design on-premises tiers separately using platforms explicitly built for that purpose rather than relying on undocumented Bedrock extensions, and do not let slide titles labeled “hybrid” conceal identity model differences.
The most expensive failure involves selecting platforms to satisfy unwritten constraints, then discovering during security review that the constraint was negotiable. This leaves organizations operating unnecessary infrastructure. The most cost-effective intervention occurs when actual controls are documented in writing before any vendor comparison begins.
First, cite vendor documentation with revision dates in front of you. Every decision-bearing fact moves on vendor publishing cycles, and one on-premises option is currently in preview. Recommendations without links and dates are undated memory wearing citations.
Second, ask which three hybrid shapes match your requirement before naming platforms. Firms opening with vendor selection rather than constraint analysis sell vendor partnerships, not architectures.
Third, require production of the actual written controls: the documented requirement from authorizing officials or frameworks stating data-residency needs. If this cannot be produced, that absence itself becomes the finding and often matters more than platform selection.
Fourth, name on-premises infrastructure operators by role before recommending hybrid designs. GPU nodes, cluster upgrades, model lifecycle, and on-call rotations need owners. Unowned components mean unexecutable plans.
Fifth, separate platform decisions from data-remediation work. Access-control cleanup on the content AI systems will read is separate scope, owners, and schedule. Burying it inside platform selection turns six-week decisions into year-long projects.
i3solutions has delivered on the Microsoft stack since 1997, with 1,500+ Microsoft engagements behind it and senior, 100 percent US-based teams working under the compliance standards regulated environments require. On hybrid AI, the discipline is the same one that runs every governance-first program here: name the pattern, document the written controls, cite the vendor evidence with its date, and design around what the platform actually supports on the day the design is signed.
Matt Lawson has spent more than 14 years at i3solutions guiding complex enterprise technology work from scope and system design through development, acceptance, and long-term support. His expertise spans technical oversight, solution architecture, SharePoint and Microsoft 365 delivery, Power Platform implementation, business intelligence, enterprise search, and the practical application of AI to solve real business and operational challenges.
Connect on LinkedInFor Microsoft-standardized regulated enterprises: Microsoft, because Azure Government receives FedRAMP High assessment and authorization and Foundry Local on Azure Local runs inference on Arc-enabled Kubernetes clusters secured with Microsoft Entra ID, placing both halves in one identity and governance plane. For genuinely disconnected or classified enclaves: Google Distributed Cloud air-gapped, which Google describes as not requiring Google Cloud connectivity, with Gemini available on the air-gapped product. For AWS-native estates: Amazon Bedrock in AWS GovCloud with AWS's named FedRAMP Class D and DoD IL4/IL5 model list, with on-premises halves designed separately on dedicated platforms.
Yes, with maturity caveats. Foundry Local on Azure Local describes deploying AI models on Arc-enabled Kubernetes clusters, keeping data processing on-premises, and operating in disconnected environments where internet connectivity is not available. However, the service remains in preview; features and capabilities may change before general availability, and deployment is by request during preview. Confirm your specific cloud path with Microsoft rather than inferring it from documentation.
Not according to reviewed AWS documentation. AWS describes Bedrock as serverless with Region-based availability. No documentation describes Bedrock inference on customer-owned hardware. This is a documentation absence rather than an explicit prohibition. If on-premises requirements are firm and AWS is your incumbent, pose this question to your AWS account team in writing and design on-premises tiers around actual answers rather than assumptions.
Google confirms this in the Google Distributed Cloud air-gapped overview, which states the product does not require connectivity to Google Cloud. Google's April 9, 2025 announcement states the air-gapped product carries authorization for US Government Secret and Top Secret missions with Gemini availability. Because public documentation contains lighter model-by-model authorization detail than Microsoft and AWS materials, obtain current model catalogs and reference architectures for your enclave directly from Google.
AWS announced on June 25, 2026 that OpenAI GPT, OpenAI GPT OSS, and NVIDIA Nemotron models have FedRAMP High and DoD IL-4/5 approval in AWS GovCloud (US). AWS's certification status page lists Titan, Claude, and Llama models carrying that authorization. Microsoft documents Azure Government as assessed and authorized at FedRAMP High with separate Azure OpenAI government endpoints. Google Cloud's guidance conditions FedRAMP High and DoD IL4/IL5 support on using models with US multi-regional endpoints inside properly configured Assured Workloads folders. Verify authorization at the specific model level for exact deployment targets.
Three issues emerge in roughly this order: the driving constraint proves to be organizational preference rather than a written compliance control, meaning on-premises infrastructure operates without actual compliance benefit; permissions on content AI systems read were already problematic, which AI surfaces at speed with citations, creating unexpected remediation projects; and governance seams between cloud and on-premises halves belong to nobody, because cloud and on-premises components answer to different owners, leaving connectors, identity, and logging ungoverned. All three surface more cost-effectively in early assessments than in security reviews.
Every agent in the estate answers for what it can reach, what it can do, and who approved it. i3solutions' senior AI advisors work with IT leaders who need that record built and enforced before an auditor asks for it.
Talk to a Senior AI Advisor
US-Based | Est. 1997
© i3solutions. All rights reserved.
US-Based | Est. 1997
© i3solutions. All rights reserved.


