
Building on Microsoft 365 GCC High changes five things about delivery: service availability, administrative identity, every connection out of the boundary, non-production environments, and audit evidence. Service availability and administrative identity behave as gates that stop a design in its current shape; the other three narrow it. Standing up the tenant is separate work performed by a certified AOS-G supplier; everything below assumes a tenant that already exists.
One question belongs here: what changes about designing, building, and integrating Microsoft solutions once the tenant you are building in is Microsoft 365 GCC High. That covers the design-time checks, the identity and administration model for the delivery team, the treatment of connections out of the boundary, the shape of non-production environments, and the evidence the build itself has to produce.
It does not choose the environment. Whether GCC High is the environment your obligations call for, and how it compares with GCC and with commercial Microsoft 365 for holding CUI, is a separate decision covered elsewhere. It does not price anything; licensing and migration economics are a separate scope, and no price appears on this page. It does not sequence a tenant-to-tenant move; that is a migration project on its own. It does not select an implementation firm. And it does not stand up the tenant: provisioning a GCC High tenant, sponsoring eligibility, and the accreditation work around both are performed by a certified AOS-G supplier. Everything below assumes a tenant that already exists and a supplier relationship already in place.
A team arriving from a commercial tenant carries a working mental model of Microsoft 365, and almost all of it survives the move. The parts that do not survive are the parts nobody thinks to check, because in a commercial tenant they were never decisions at all.
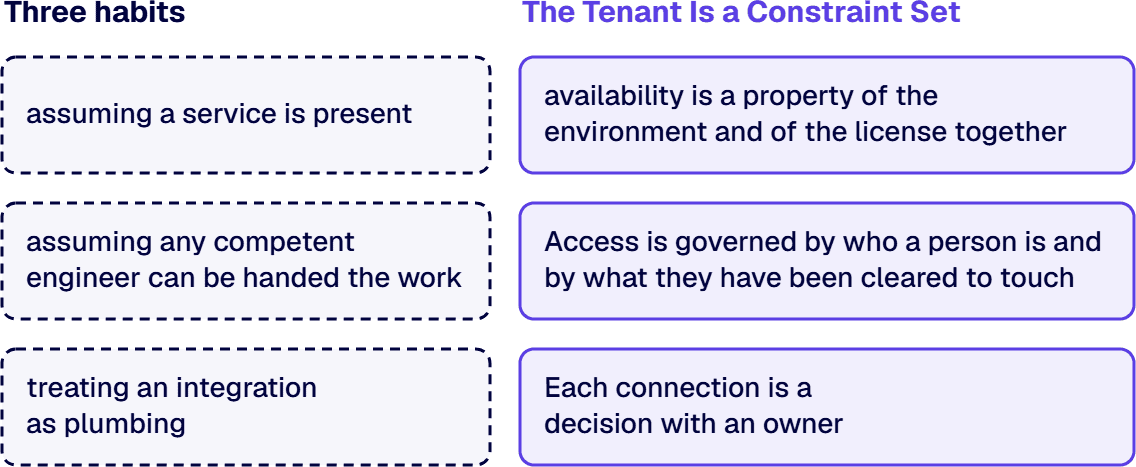
Three habits are worth naming, because each one produces a different late failure. The first habit is assuming a service is present. In a commercial tenant, a service the design calls for is switched on or it is a licensing conversation. In a sovereign environment, availability is a property of the environment and of the license together, and it varies by service and over time. The design-time question stops being “do we have the license” and becomes “is this service available to us here, on the day we go to configure it, and where did we read that.”
The second habit is assuming any competent engineer can be handed the work. Access to the tenant is governed by who a person is and by what they have been cleared to touch, and that is a property of the person and their employer, not of the ticket. A design that is fine on paper can be undeliverable by the team that wrote it.
The third habit is treating an integration as plumbing. A connection from the tenant to a line-of-business system, an engineering system, or another cloud is the point where data crosses the boundary the tenant exists to hold. Each connection is a decision with an owner, and it belongs on the design, not in a configuration screen. Those three habits produce the five decisions below.
| # | Decision | The question, asked at design time | Where the answer is read from | Behavior |
|---|---|---|---|---|
| 1 | Service availability | Is every service this design depends on available to us in this environment, under the licenses we hold? | Microsoft’s own service description and admin center for this environment, read on the day, and recorded with that date. | GATE |
| 2 | Administrative identity | Who may hold an account in this tenant, at what level of privilege, and does that set include everyone this design needs? | The tenant’s own identity and privileged-access configuration, plus the personnel terms in the contract. | GATE |
| 3 | Connections out of the boundary | For every connection this design makes outside the tenant, what crosses it, in which direction, and who owns that decision? | The design’s own integration inventory, signed by a named owner per connection. | NARROWS |
| 4 | Non-production environments | Where do development and test environments live, and what may be inside them? | The environment inventory and the data-handling terms that govern each copy. | NARROWS |
| 5 | Audit evidence | What does this build have to be able to show afterwards, and which artifact shows it? | The evidence list agreed at design time, mapped to the artifact the build already produces. | NARROWS |
Decisions 1 and 2 are gates: a design that fails either one does not proceed to build in its current shape, and no strength elsewhere offsets that. Decisions 3, 4, and 5 narrow: they change what the design is allowed to do without stopping it. Where 3, 4, and 5 conflict with each other, the connection decision wins, because a connection that should not exist cannot be made acceptable by better evidence or a tidier environment.
The check is small and it has to be written down. For each service the design depends on, confirm availability for this specific environment and for the licenses actually held, read from Microsoft’s published service description for that environment and from the tenant’s own admin center. Record what you read and the date you read it.
The date is the part teams skip, and it is the part that matters. Availability in a sovereign environment moves over time, and a design that was correct when it was written can be wrong by the time it is built. A confirmation with no date attached cannot be re-checked, so it has to be re-done, and it usually gets re-done by an engineer under deadline pressure who assumes the design was right.
Two secondary questions belong in the same pass, because they fail the same way. Where the design depends on a connector, an add-in, or a third-party component, confirm the same thing about that component and about the vendor’s support for it in this environment. And where the design assumes an integration point exposed by a service, confirm the integration point itself, since a service being present does not establish that every surface on it is. What a pass looks like: a list, one row per dependency, each row carrying the source read and the date read.
i3solutions’ consulting practice covers estate strategy, delivery capacity, discovery, and program execution for regulated enterprises on the Microsoft stack.
Two questions sit underneath this one, and teams commonly answer the first and discover the second. The first is the tenant’s own access model: which roles exist, who holds them, how privilege is elevated for a piece of work, and how it is given back. That is ordinary Microsoft 365 privileged-access design, read from the tenant’s configuration.
The second is who is eligible to hold an account at all. In a regulated tenant this is a property of the person and of their employer, and it is set by the contract and the obligations behind it. It reaches subcontractors, it reaches anyone brought in for a short piece of specialist work, and it reaches the vendor support arrangements the design assumes.
The failure this produces is specific. A design gets written by people who can see the tenant, and a piece of it gets assigned to somebody who cannot be given access. The work then either stalls or gets routed around, and the routing around is the part that shows up in an audit. The check, asked at design time: for each piece of work this design implies, name the role that performs it and confirm that a person eligible to hold that role is available to do it. Where the answer is no, the design changes shape, and it changes shape now.
Delivery at i3solutions is senior and 100 percent US-based. That is stated here because eligibility is the constraint this decision turns on: a delivery model that depends on people who cannot be given accounts in the tenant is a delivery model that does not fit this environment. Confirm the same thing about every party the design depends on, including any subcontractor and any vendor support path.
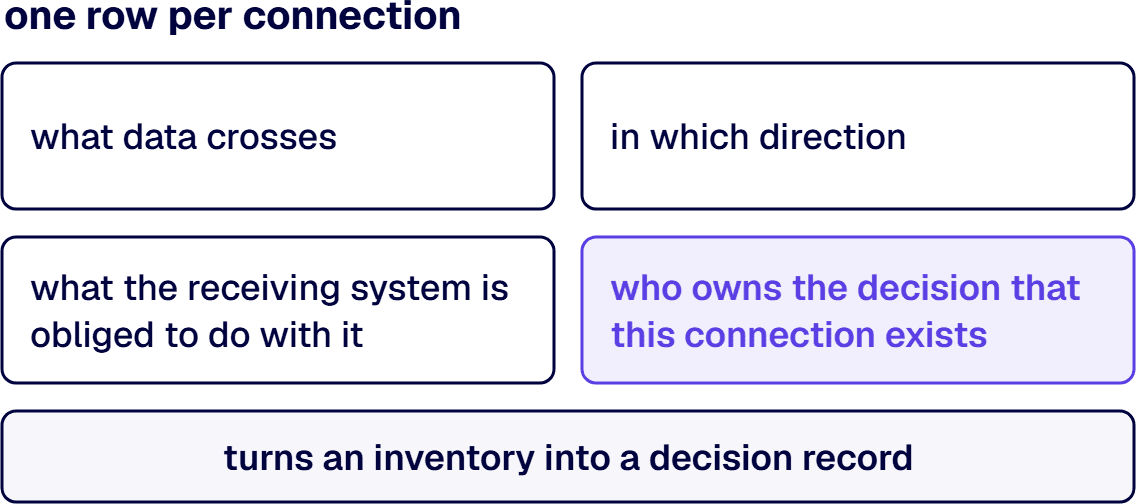
The tenant exists to hold a boundary. An integration is where something crosses it, and a build usually creates several. Take an inventory at design time, one row per connection, and answer four things about each: what data crosses, in which direction, what the receiving system is obliged to do with it, and who owns the decision that this connection exists. The fourth field is the one that turns an inventory into a decision record, and it is the one most often left blank.
Three shapes recur and each carries a different question. A connection to a line-of-business system inside the same organization is usually the easiest to justify and the easiest to under-specify, because everyone assumes the obligations travel with the data automatically. Confirm what the receiving system is obliged to do, in writing, per connection. A connection to an engineering system or to another cloud is where the boundary genuinely changes hands. The question is not whether the connection is technically possible; the question is whether the receiving environment carries obligations that match the ones the data arrived with. A connection out to a vendor service, including a service the design uses for monitoring, translation, enrichment, or any other convenience, is the one that gets added late by an engineer solving a small problem. The inventory has to be a living artifact for exactly that reason, and a change to it is a design change.
Development and test environments are where regulated data most often ends up somewhere nobody decided it should be, and the mechanism is mundane. A team needs realistic data to test against, production is the only place realistic data lives, and copying it is a two-minute operation that no gate stands in front of.
Three questions settle this at design time. Where does each non-production environment physically live, and is it inside the same boundary as the tenant it serves? A development environment standing outside the boundary is a design decision, and it is only defensible if it was taken deliberately and if what is allowed into it is written down. What may be inside each one? The workable answer is usually a manufactured dataset that exercises the same shapes as production and carries none of the content that made production sensitive. Building that dataset is real work and belongs in the plan, since a team that has not been given one will improvise. Who may reach each one, and does that set match the eligibility answer from decision 2? A non-production environment with a looser access model than the tenant it mirrors is the same problem as a looser boundary, arriving through a door nobody was watching.
Everything built inside a regulated tenant eventually has to be explained to somebody. The explanation is cheap if the build produced it as it went and expensive if it has to be reconstructed from memory and change tickets months later.
Agree the evidence list at design time, and keep it short enough that it survives contact with delivery. Four items cover most of what gets asked for: what was configured and by whom, what was granted to whom and for how long, what data each integration moves, and what was tested before release. Map each item to an artifact the build already produces, so the evidence falls out of the work and never becomes a separate task competing with delivery. The mapping is the whole trick. A deployment pipeline already records what was deployed and when. A privileged-access process already records elevations. The integration inventory from decision 3 already records what crosses the boundary. Naming those artifacts as the evidence, at design time, converts three things that already exist into an answer, and it exposes the gaps while there is still time to close them.
The division is worth stating plainly, because a proposal that blurs it is a proposal that will be wrong about something later. Standing up a GCC High tenant, sponsoring the eligibility that makes it possible, and the accreditation work around both are performed by a certified AOS-G supplier. That is their work and i3solutions does not do it. i3solutions works alongside it.
i3solutions engages its Federal Compliance Assessment when the scope spans a FedRAMP Moderate or FedRAMP High boundary, or when the client operates in a GCC High tenant.
What we do is the work on top: designing solutions that fit the environment, building them, integrating the tenant with the systems around it, and producing the evidence that the build behaved as designed. On an estate that is part sovereign and part something else, that includes the integration work across the join, because a regulated tenant is rarely the whole picture. The practical consequence for a plan is that two parties appear on it. A plan that shows only one of them has either absorbed somebody else’s work or quietly assumed it is finished.
Three situations send you elsewhere, and recognizing them early saves a scoping conversation that goes nowhere. If the environment decision is still open, the framework on this page will not help you take it, and taking it with a delivery lens produces a bad answer; start with an environment comparison instead. If the tenant does not exist yet, the next call is to a certified AOS-G supplier, and the design work described here begins after theirs. If the immediate problem is a move of an existing estate, a migration guide owns that sequence; this page describes what changes for the projects that come afterwards.
Michael Branson co-founded i3solutions 30 years ago and brings executive, operational, and technical perspective to organizations working in complex, secure, and mission-critical environments. His insights focus on business process consulting, automation, data analytics, collaboration, secure operating models, and the operational discipline required to turn technology investments into practical business systems with measurable value.
Connect on LinkedInFive decisions change, and none of the five is an engineering problem. Service availability becomes a design input confirmed for this environment and these licenses on a recorded date, since availability is a property of the environment and not only of the license. Administrative identity becomes a question of who is eligible to hold an account at all, which is set by the contract and reaches subcontractors and vendor support paths. Every connection out of the boundary becomes a named decision with an owner, recorded in an integration inventory. Non-production environments become part of the boundary, which makes their location, permitted contents, and access model design decisions. Audit evidence becomes a by-product the build is designed to produce, mapped at design time to artifacts the build already generates.
Service availability and administrative identity behave as gates, and the other three narrow a design without stopping it. A design that depends on a service unavailable in this environment does not proceed in its current shape, and no strength elsewhere offsets that. A design that requires work from people who cannot be given accounts in the tenant is undeliverable by that team, and it changes shape at design time or it stalls at build time. Connections out of the boundary, non-production environments, and audit evidence change what a design is allowed to do. Where those three conflict with one another, the connection decision wins, because a connection that should not exist cannot be made acceptable by better evidence or a tidier test environment.
Read it, for this specific environment and for the licenses actually held, from Microsoft's published service description for that environment and from the tenant's own admin center, and record both what you read and the date you read it. The date is the load-bearing part, because availability in a sovereign environment moves over time and a design that was correct when written can be wrong when built. Two secondary checks belong in the same pass. Where a design depends on a connector, an add-in, or a third-party component, confirm the vendor's support for it in this environment as well as its presence. And where a design depends on an integration surface exposed by a service, confirm that surface specifically, since a service being present does not establish that everything on it is.
Two separate questions decide this, and answering only the first is the common failure. The first is the tenant's own access model: which privileged roles exist, who holds them, how privilege is elevated for a piece of work, and how it is given back. The second is eligibility, meaning who may hold an account at all, which is a property of the person and their employer set by the contract and the obligations behind it, and which reaches subcontractors, short-term specialists, and vendor support arrangements. The design-time check is to name the role that performs each piece of work the design implies, then confirm that a person eligible to hold that role is available to do it.
Settle three questions at design time. Where each non-production environment physically lives, and whether it sits inside the same boundary as the tenant it serves; an environment standing outside that boundary is a legitimate design decision only when it was taken deliberately and what is allowed into it is written down. What may be inside each one, where the workable answer is usually a manufactured dataset that exercises the same shapes as production while carrying none of the content that made production sensitive. And who may reach each one, checked against the same eligibility answer that governs the tenant, since a non-production environment with a looser access model is the same exposure arriving through a door nobody was watching.
No. Standing up a Microsoft 365 GCC High tenant, sponsoring the eligibility that makes it possible, and the accreditation work around both are performed by a certified AOS-G supplier, and we work alongside that supplier. Our work is what sits on top of a tenant that already exists: designing solutions that fit the environment, building them, integrating the tenant with the line-of-business systems, engineering systems, and other clouds around it, and producing the evidence that the build behaved as designed. A plan for this kind of program therefore shows two parties, and a plan showing only one has either absorbed somebody else's work or assumed it is already finished.
CMMC levels, cloud environment boundaries, and data classification decide what an assessment covers long before an assessor arrives. i3solutions' senior governance advisors work with enterprise IT leaders who want those scoping decisions made deliberately.
Schedule a Governance Scoping Discussion
US-Based | Est. 1997
© i3solutions. All rights reserved.
US-Based | Est. 1997
© i3solutions. All rights reserved.


