By Scot Johnson, Founder / CEO, i3solutions. Scot Johnson co-founded i3solutions 30 years ago with a focus on expert-led delivery, strategic advisory, and complex Microsoft-centered solutions for organizations where technology decisions carry operational, financial, and mission risk.
To govern citizen-developer Power Apps that IT has inherited, run the takeover in three moves: inventory every app and flow with its real business criticality, triage which apps IT formally adopts versus retires versus leaves in a bounded personal-productivity tier, and then put the adopted apps under the same governance a regulated enterprise applies to anything in production: environment strategy, data loss prevention policies, application lifecycle management, named decision rights, monitoring, license alignment, and compliance mapping. The mistake is treating this as a one-time cleanup. Citizen development does not stop when IT takes ownership; governance has to be the standing structure that decides where the next app lands.
That is the answer in three moves and a warning. The rest of this page is the takeover sequence in order, the triage rule that keeps it honest, and what changes for the citizen developers themselves, because a governance program that reads as confiscation loses the builders who were solving real problems.
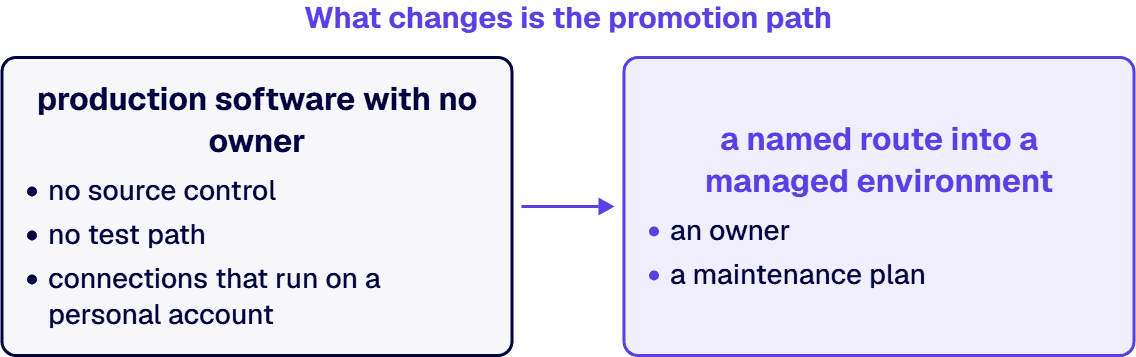
The pattern is consistent: a business user builds an app in the default environment to fix a real process gap, the process comes to depend on it, and the author changes roles or leaves. At that moment the app is production software with no owner, no source control, no test path, and connections that run on a personal account. Multiply by a few years of enthusiastic building and IT inherits an estate it cannot see, cannot maintain, and is nonetheless accountable for. The instinct to shut it all down is wrong twice: it destroys working business processes, and it pushes the next generation of apps further into the shadows.
A Power Platform governance framework is the policy structure governing how Power Apps, Power Automate, and Dataverse are used across an enterprise. It is not a Center of Excellence toolkit installation and not a list of admin-center settings. It defines who can build what, under which controls, and with what audit evidence, with each component owned by a named role. The framework design itself is covered in depth on our Power Platform governance page, and if this takeover is happening because an audit already flagged the estate, the audit-flagged remediation path sequences the findings first.
Governed does not mean closed. The personal-productivity tier stays open for genuinely personal tools, with DLP boundaries that keep business data out of ungoverned connectors. What changes is the promotion path: an app that a team starts depending on has a named route into a managed environment, an owner, and a maintenance plan, instead of a quiet slide into being critical and unsupported. i3solutions runs a governed Power Platform for a federal defense agency supporting roughly 10,000 personnel across about 180 locations, which works because it is governed, not despite it.
No. Closing the default environment outright destroys working business processes and drives building underground. Bound it instead: DLP policies that keep business-critical connectors out, a size and dependency threshold that triggers review, and a named promotion path for apps that graduate. Our page on Power Apps for a Business-Critical Enterprise Application walks through the four conditions that decision needs: Dataverse as the data platform, solution-based release control, named support ownership, and licensing sized to the user population.
Inventory first, then ask the process owners, not the app authors. Usage telemetry identifies candidates, but the deciding question is whether a business process stalls when the app breaks. Those apps are production software regardless of who built them.
Usually not immediately. The first pass is stabilization: move the app to a managed environment, replace personal-account connections with service principals, and put it in a solution under source control. Rebuild decisions come later, per app, based on criticality and maintainability rather than on principle.
Standing structure rather than cleanup: environment strategy that decides where new apps land, DLP that travels with data sensitivity, monitoring that surfaces new apps weekly, and named decision rights for exceptions. Governance that runs as a program absorbs new citizen development instead of being surprised by it.
The bounded personal tier keeps low-stakes building fast, and the promotion path is what keeps high-stakes apps alive. What actually slows a business down is the ungoverned alternative: an unowned app failing mid-process, or a connector policy change taking out a workflow nobody knew existed.
Yes, if it runs as a governed program with named ownership. i3solutions runs a governed Power Platform for a federal defense agency supporting roughly 10,000 personnel across about 180 locations. Scale is an argument for the framework, not against it.
US-Based | Est. 1997
© i3solutions. All rights reserved.
US-Based | Est. 1997
© i3solutions. All rights reserved.


